Privileged Access Management for AI Agents: Zero Trust
Privileged Access Management for AI Agents: Zero Trust
Privileged Access Management for AI Agents: Zero Trust
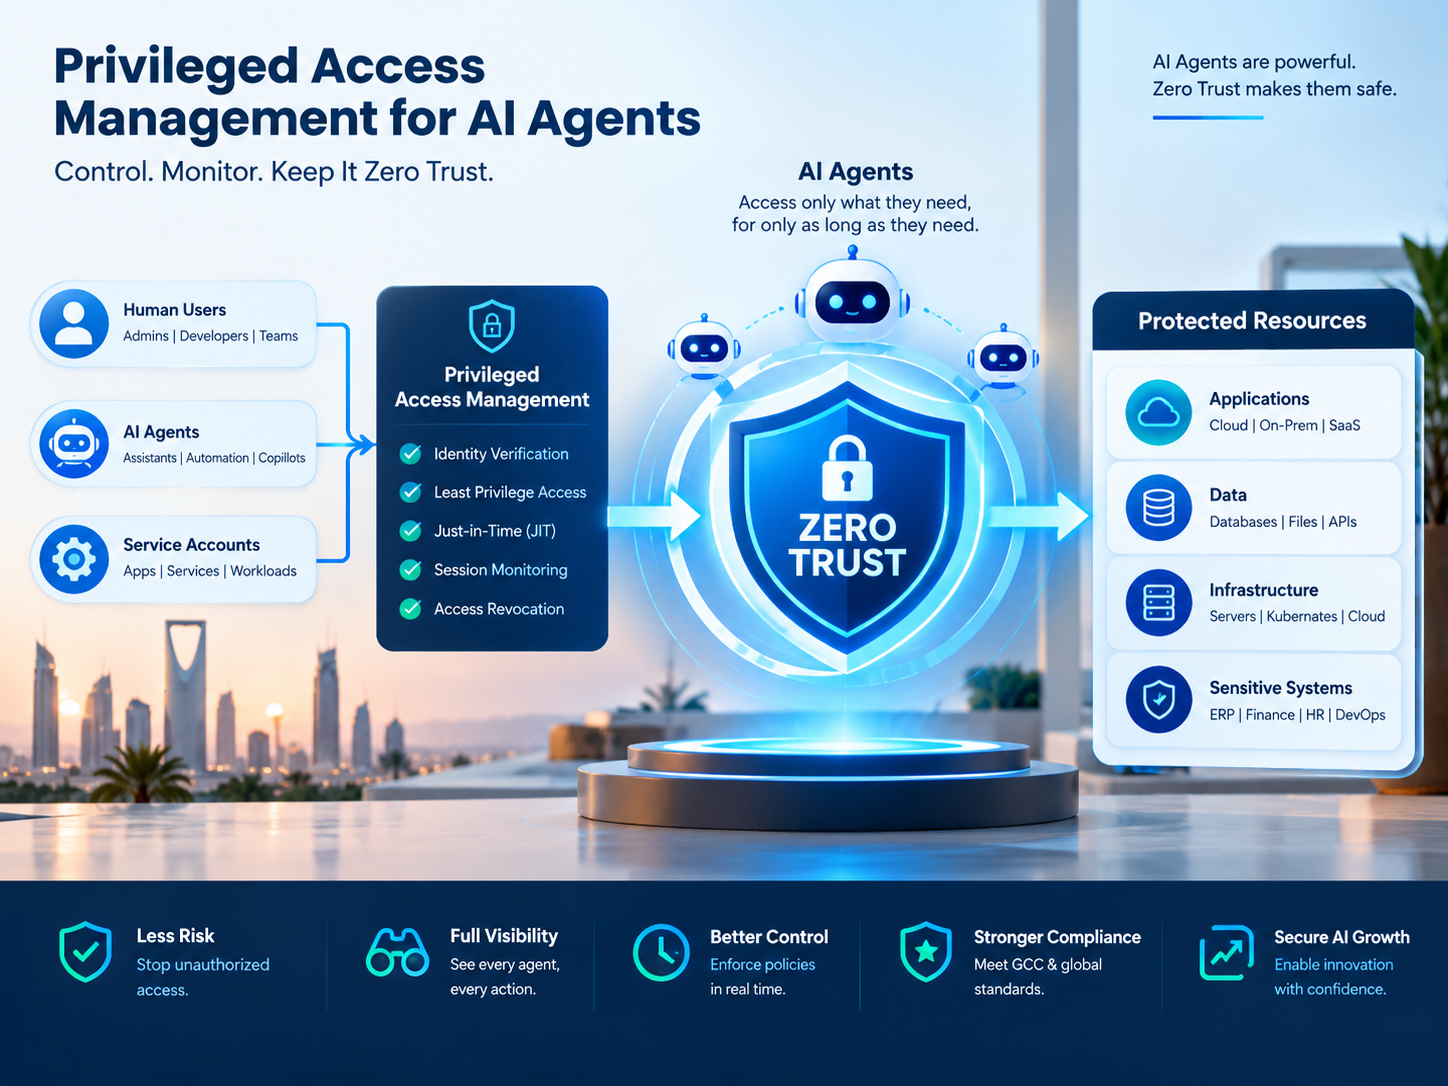
Privileged access management for AI agents controls how autonomous agents receive, use, and lose access to sensitive systems, APIs, data, and administrative tools.
A strong agentic PAM model combines unique machine identities, least privilege, just-in-time (JIT) access, short-lived credentials, runtime authorization, continuous monitoring, and automatic revocation. The goal is simple: give an AI agent only the authority it needs, only when it needs it, and keep every privileged action attributable and auditable.
AI agents are quickly becoming privileged identities in their own right. Unlike traditional software that mainly responds to predefined inputs, autonomous agents can call APIs, query databases, operate cloud resources, invoke MCP servers, trigger workflows, and make business decisions.
That changes the identity-security model. Privileged access management for AI agents must control not only who or what authenticates, but also which actions an agent can perform, why it has that authority, how long the authority lasts, and what happens when the task ends.
The scale of identity threats makes those controls increasingly important. Microsoft reported more than 600 million identity attacks per day in its 2024 security reporting. Verizon’s 2025 Data Breach Investigations Report (DBIR) reported credential abuse in roughly 22% of breaches as an initial access vector.
What Is Privileged Access Management for AI Agents?
Privileged access management for AI agents is the set of security controls used to authenticate autonomous agents, authorize high-impact actions, broker credentials, restrict permissions, monitor activity, and revoke access when a task or agent lifecycle ends.
In practice, it extends familiar PAM principles beyond human administrators to dynamic non-human identities (NHIs).
When Does an AI Agent Become a Privileged Identity?
An AI agent becomes privileged when its authority can materially affect systems, sensitive data, money, security, or business operations.
That can include.
Modifying production infrastructure
Reading sensitive customer or employee records
Invoking administrative APIs
Approving or initiating transactions
Changing system configurations
Operating privileged tools
Accessing production databases or cloud resources
Privilege is therefore about authority and potential impact, not whether the identity is human.
AI Agents vs Service Accounts and Other Non-Human Identities
Service accounts, certificates, workloads, API keys, and other machine identities are generally designed around predictable operations. AI agents introduce a different challenge because they can dynamically choose tools, construct actions, delegate tasks, and operate at machine speed.
Agentic identity security therefore requires more context. Security teams need to know not only which agent is acting, but also its current task, delegated authority, available tools, downstream resources, and runtime behavior.
For related identity architecture, see Mak It Solutions’ AI Agent Identity Management Guide and AI Agent Identity Security Guide.
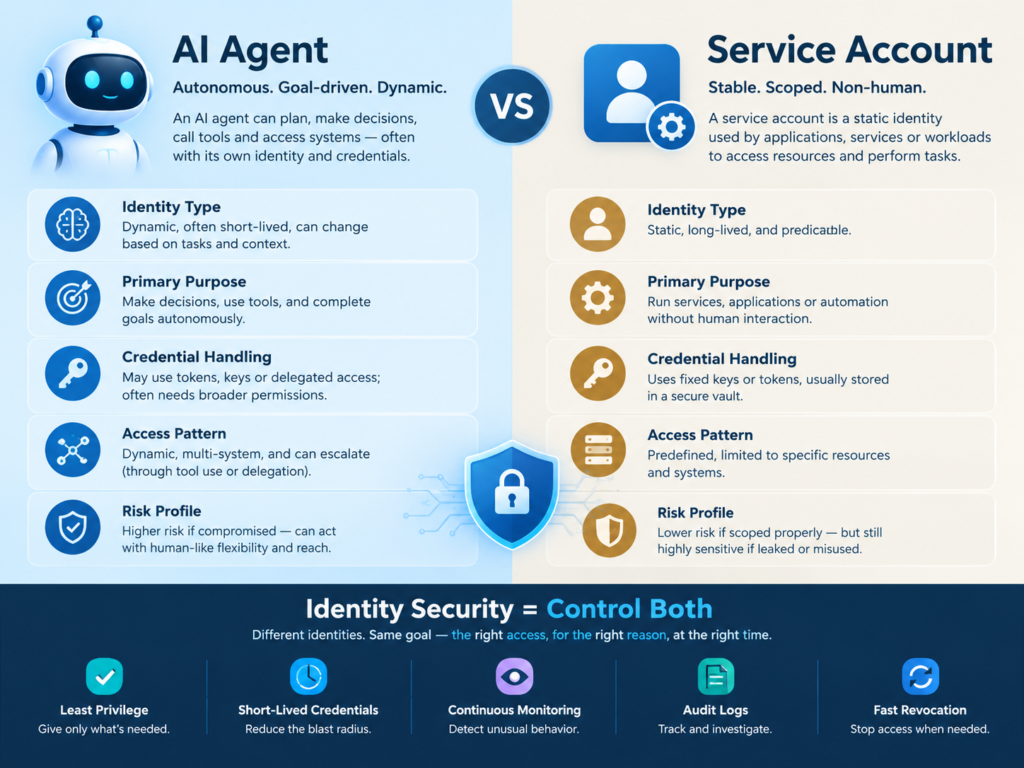
PAM vs IAM vs IGA for Autonomous Agents
IAM, IGA, and PAM solve related but different parts of the problem.
IAM establishes identities, authenticates them, and provides access. IGA governs identity lifecycle, ownership, entitlements, reviews, and accountability. PAM focuses on protecting high-impact credentials, permissions, resources, and actions.
For autonomous agents, these capabilities work best as complementary layers. Agentic IAM establishes who the agent is, IGA governs its lifecycle and entitlements, and agentic PAM tightly controls its privileged activity.
Why Traditional PAM Falls Short for Autonomous AI Agents
Traditional PAM commonly assumes relatively predictable human sessions and stable relationships between accounts and resources.
Autonomous agents may run continuously, switch between tools, delegate work to other agents, and request permissions dynamically. That makes task-scoped authorization and machine-speed security decisions far more important.
Persistent Credentials and Excessive Permissions
Long-lived API keys, OAuth tokens, embedded secrets, and broadly privileged service accounts increase the potential blast radius if credentials are exposed or misused.
Git Guardian reported approximately 12.8 million new secret occurrences detected on public GitHub during 2023.
AI agents should obtain credentials through controlled vaulting or credential brokering rather than storing powerful secrets directly in prompts, code, workflows, or configuration files.
Machine-Speed Actions and Agent-to-Agent Delegation
Multi-agent systems introduce chains of authority.
For example, Agent A may instruct Agent B to invoke an MCP tool that ultimately changes a cloud resource. The final API request alone does not tell the complete story.
Security controls should preserve that delegation chain so an organization can determine.
Which identity initiated the action
Which agents participated
Which agent executed the privileged operation
What permission or credential was used
Which policy authorized the action
Without that context, accountability becomes difficult precisely when systems are operating at their fastest.
Shadow Agents, Audit Gaps, and Human Accountability
Unregistered AI agents can become the machine equivalent of shadow IT.
Every production agent should have an inventory record, defined owner or human sponsor, approved purpose, entitlement boundaries, lifecycle status, and reliable audit history.
Dormant, abandoned, or orphaned agents should not retain privileged access indefinitely.
How to Enforce Least Privilege and JIT Access for AI Agents
Effective privileged access management for AI agents starts with a straightforward principle: give every agent a distinct identity, authorize only what its current task requires, issue credentials only when needed, and revoke privilege when the task ends.
Give Every Agent a Unique, Governed Identity
Avoid placing several autonomous agents behind one shared service account.
A distinct workload or machine identity makes authorization, monitoring, incident investigation, and lifecycle management much clearer. That identity should also connect to an owner, application, environment, approved purpose, and expiry or review policy.
Use Just-in-Time Access and Zero Standing Privilege
Just-in-time access for AI agents replaces permanently elevated permissions with temporary privilege.
Before granting elevation, a policy engine can evaluate factors such as.
Agent identity
Requested action
Target resource
Current task
Risk context
Delegated authority
Environment
For least-privilege AI agents, elevated permissions should expire automatically rather than remain available for the next task.
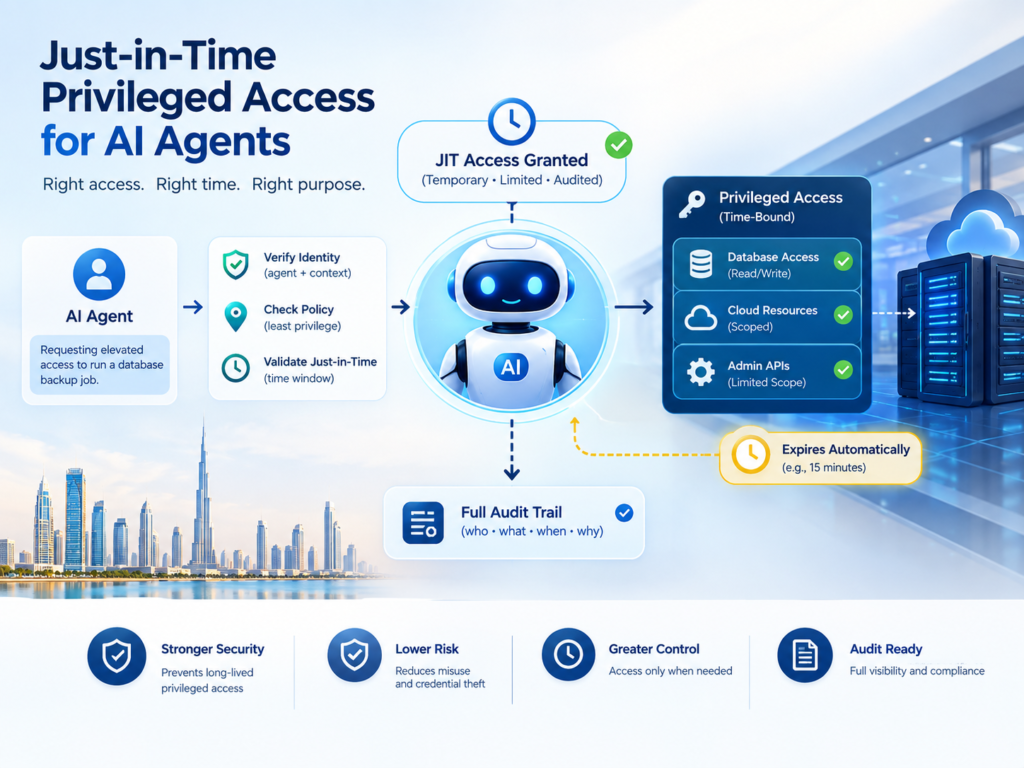
Replace Persistent Secrets With Short-Lived Credentials
Credential brokers can issue ephemeral OAuth tokens, cloud credentials, certificates, or API credentials only after authorization succeeds.
This reduces long-term credential exposure while making rotation and revocation easier to manage.
Mak It Solutions’ Back-End Development Services cover authentication, authorization, databases, and API integrations relevant to building controlled application architectures.
A Zero Trust Architecture for Privileged AI Agents
Zero Trust for AI agents means identity alone does not provide blanket permission.
Each sensitive request should be evaluated against the agent’s identity, task, target resource, context, requested privilege, applicable policy, and delegated authority before execution.
NIST’s Zero Trust architecture rejects implicit trust based solely on network location or asset ownership and emphasizes authentication and authorization around resources.
Authenticate the Agent and Validate Delegated Authority
Authentication answers.
“Which agent is this?”
Runtime authorization answers a more important operational question:
“May this agent perform this action on this resource right now?”
For delegated workflows, authorization should also validate the originating principal and delegation chain rather than trusting whichever agent happens to make the final API call.
Enforce Policy at APIs, Cloud Resources, and MCP Servers
Policy enforcement should sit close to sensitive resources, including.
APIs
SaaS platforms
Databases
AWS, Azure, and GCP workloads
Administrative interfaces
MCP servers
Privileged tools
This creates a useful separation between an AI agent’s reasoning and the organization’s security decision.
The agent can request an action. Independent security policy decides whether that action is allowed.
Monitor, Audit, and Revoke Privileged Agent Activity
Security teams should record authentication events, authorization decisions, privilege elevation, credential issuance, tool calls, delegation events, resource changes, and revocation.
Reliable logs support anomaly detection, incident investigation, compliance evidence, and accountability. They also allow security teams to terminate privileges quickly when an agent operates outside its expected boundaries.
Compliance Requirements Across the USA, UK, Germany, and EU
PAM can support access control, accountability, monitoring, and evidence requirements across regulated environments. However, implementing PAM by itself does not establish regulatory compliance.
USA.
Organizations in New York, San Francisco, Washington DC, and other US markets can map agent-access controls to NIST Zero Trust concepts, SOC 2 controls, PCI DSS requirements, and applicable sector-specific obligations.
For healthcare environments, the HHS HIPAA Security Rule requires appropriate administrative, physical, and technical safeguards for electronic protected health information, including relevant access and audit controls.
UK.
London financial-services organizations, Open Banking participants, SaaS providers, and NHS-related environments need identity governance and auditability appropriate to their regulatory context.
The UK Information Commissioner’s Office states that UK GDPR requires appropriate technical and organisational security measures, including controls around access to personal data.
Germany and EU.
Organizations operating in Frankfurt, Munich, Berlin, Paris, Amsterdam, Dublin, and elsewhere in the EU should consider GDPR/DSGVO requirements, applicable data-residency considerations, NIS2, and relevant EU AI Act obligations.
Financial entities may also face DORA requirements and, in Germany, applicable BaFin supervision.
DORA addresses ICT risk and operational resilience, while NIS2 establishes cybersecurity requirements for covered EU entities. The EU AI Act entered into force in August 2024 and applies obligations according to factors including the AI system’s risk category and the organization’s role.
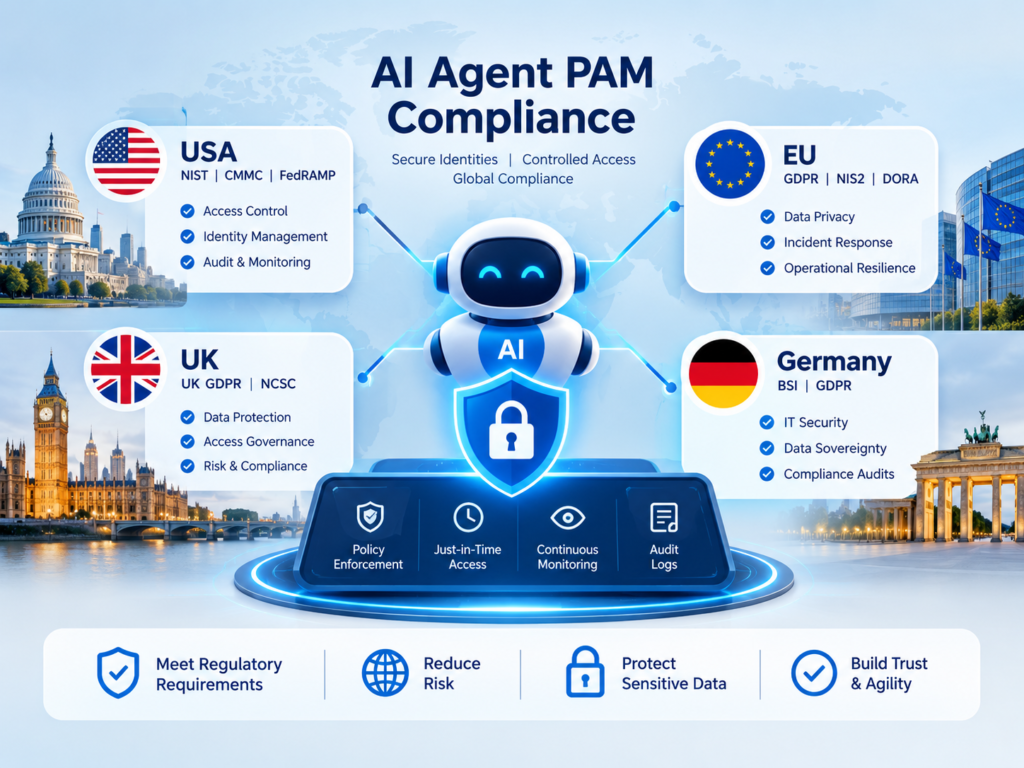
How to Evaluate a PAM Solution for AI Agents
When evaluating agentic PAM, focus on whether the platform can identify agents individually, minimize standing privilege, make runtime authorization decisions, preserve delegation context, and generate usable security evidence.
Identity, Credential, and JIT Access Capabilities
Look for capabilities such as.
Agent discovery and inventory
Unique machine identities
Credential brokering
Short-lived credentials
Secrets management
JIT privilege elevation
Automatic expiration
Zero standing privilege
These controls reduce dependence on persistent credentials and make privileged access easier to attribute.
Runtime Authorization, Delegation, and MCP Controls
Strong solutions should support fine-grained, context-aware authorization around tools and resources, including MCP access.
Security enforcement should remain independent of the agent’s own reasoning. An agent should not be able to grant itself additional authority simply because it determines that the authority would help complete a task.
Delegated agent-to-agent workflows should also remain attributable from the original requester through the final privileged action.
Governance, Integrations, and Audit Evidence
Evaluate compatibility with existing PAM, IAM, IGA, identity providers, SIEM/SOC tooling, cloud platforms, APIs, and regional compliance processes.
IBM reported the global average cost of a data breach at approximately $4.88 million in 2024. That makes integration, monitoring, and incident evidence practical business requirements—not merely architectural details.
Building a Practical AI Agent PAM Strategy
A practical PAM strategy moves an organization from unknown machine privilege toward attributable, temporary, policy-controlled access.
Discover Agents and Map Privileged Access First
Start by inventorying:
Autonomous AI agents
Service accounts
Workload identities
API credentials
MCP connections
Cloud permissions
Sensitive resources
Existing privilege paths
Each production identity should connect to an accountable owner and a documented business purpose.
Mak It Solutions’ Business Intelligence Services can complement this work where organizations need stronger operational visibility and analytics.
Prioritize High-Risk Actions and Remove Standing Privilege
Focus first on systems where misuse would have the greatest impact, such as production infrastructure, sensitive databases, payment environments, healthcare information, financial systems, administrative APIs, and security-control configurations.
For transaction-heavy platforms, Mak It Solutions also provides E-Commerce Development Services, while its Web Development Services support broader custom application requirements.
Move From Static Access to Policy-Driven Agent Authorization
A practical maturity path looks like this:
Discover → Identify → Authenticate → Authorize → Issue JIT Privilege → Monitor → Revoke → Audit
The objective is not to stop autonomous agents from acting. It is to make powerful actions attributable, narrowly authorized, observable, temporary, and revocable.
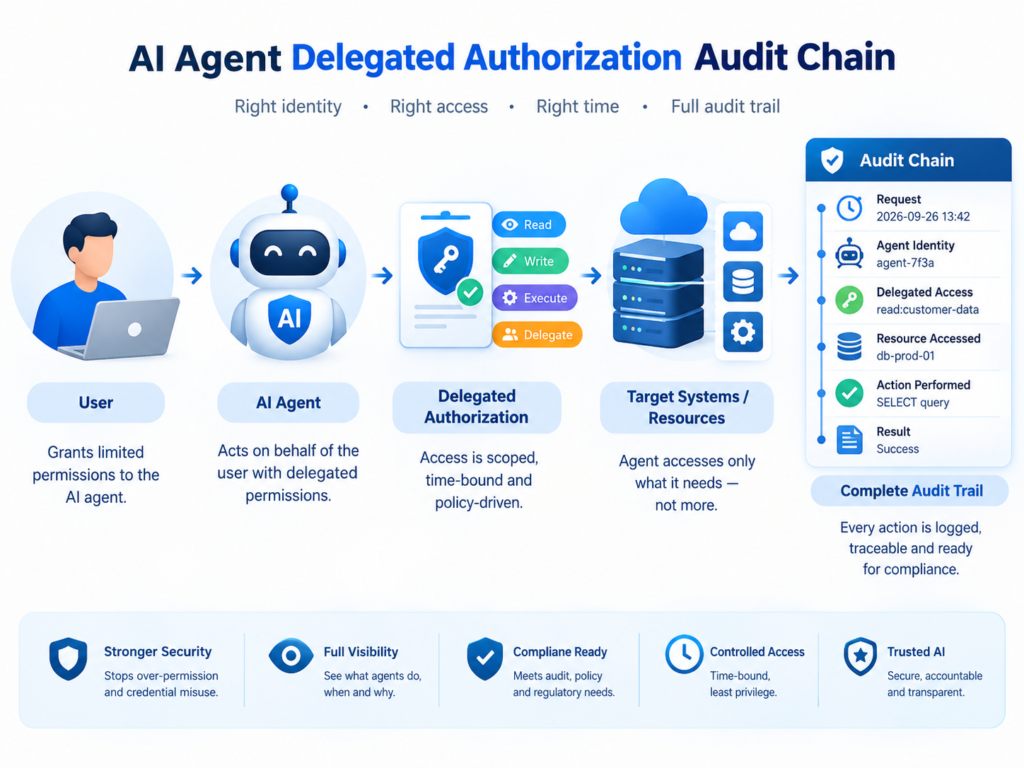
Concluding Remarks
As AI agents move from experiments into production, their access to sensitive systems becomes an identity-security issue not simply an AI deployment issue.
Effective privileged access management for AI agents combines unique identities, least privilege, JIT access, short-lived credentials, runtime authorization, delegation tracking, monitoring, and automatic revocation. ( Click Here’s )
Start by mapping where your agents can reach sensitive resources and where standing privilege still exists. From there, organizations can move toward a model in which every powerful machine action is attributable, policy-controlled, temporary, observable, and revocable.
Explore Mak It Solutions‘ technology services or request a scoped architecture review to identify practical opportunities for unique agent identities, JIT privilege, runtime authorization, and auditable access.
Key Takeaways
Privileged access management for AI agents treats autonomous agents as governed identities rather than implicitly trusted software components.
Unique identities, least privilege, JIT access, and short-lived credentials reduce persistent privilege.
Runtime authorization should evaluate the specific task, resource, context, requested action, and delegated authority.
MCP servers, APIs, databases, SaaS applications, and cloud infrastructure need policy enforcement close to the protected resource.
Audit trails should preserve agent-to-agent delegation and connect production agents to accountable owners.
PAM can support HIPAA, UK GDPR, DORA, NIS2, PCI DSS, and related governance requirements, but PAM alone does not establish compliance.
FAQs
Q : Can AI agents safely use existing service accounts?
A : They can technically use service accounts, but shared, long-lived accounts weaken attribution and may grant more privilege than a specific task requires. A stronger architecture gives production agents distinct workload identities and uses controlled delegation or credential brokering where legacy service accounts cannot immediately be replaced.
Q : Should every AI agent have its own machine identity?
A : Production agents with sensitive access generally benefit from distinct, governed identities. The appropriate granularity may vary by agent, environment, workload, or task, but shared identities should not prevent security teams from determining which agent performed a privileged action.
Q : How long should privileged credentials for AI agents remain valid?
A : There is no universal duration. Credentials should remain valid only for as long as the authorized task reasonably requires. High-risk operations may justify credentials lasting minutes or a single transaction, while longer workflows may need controlled renewal.
Q : Can AI agents access production systems without human approval?
A : They can where organizational policy permits automated authorization, but autonomous access should not mean uncontrolled access. Low-risk, well-defined actions may be authorized automatically, while destructive, unusual, high-value, or regulated actions may require human approval.
Q : How do you audit actions performed by multiple cooperating AI agents?
A : Preserve a traceable delegation chain across the workflow. Logs should connect the originating user or system, participating agents, authorization decisions, issued credentials, tools invoked, target resources, resulting actions, and revocation events. Correlation or trace IDs can help reconstruct distributed multi-agent activity.