AI Risk Register: Practical GCC Guide & Template
AI Risk Register: Practical GCC Guide & Template
AI Risk Register: Practical GCC Guide & Template
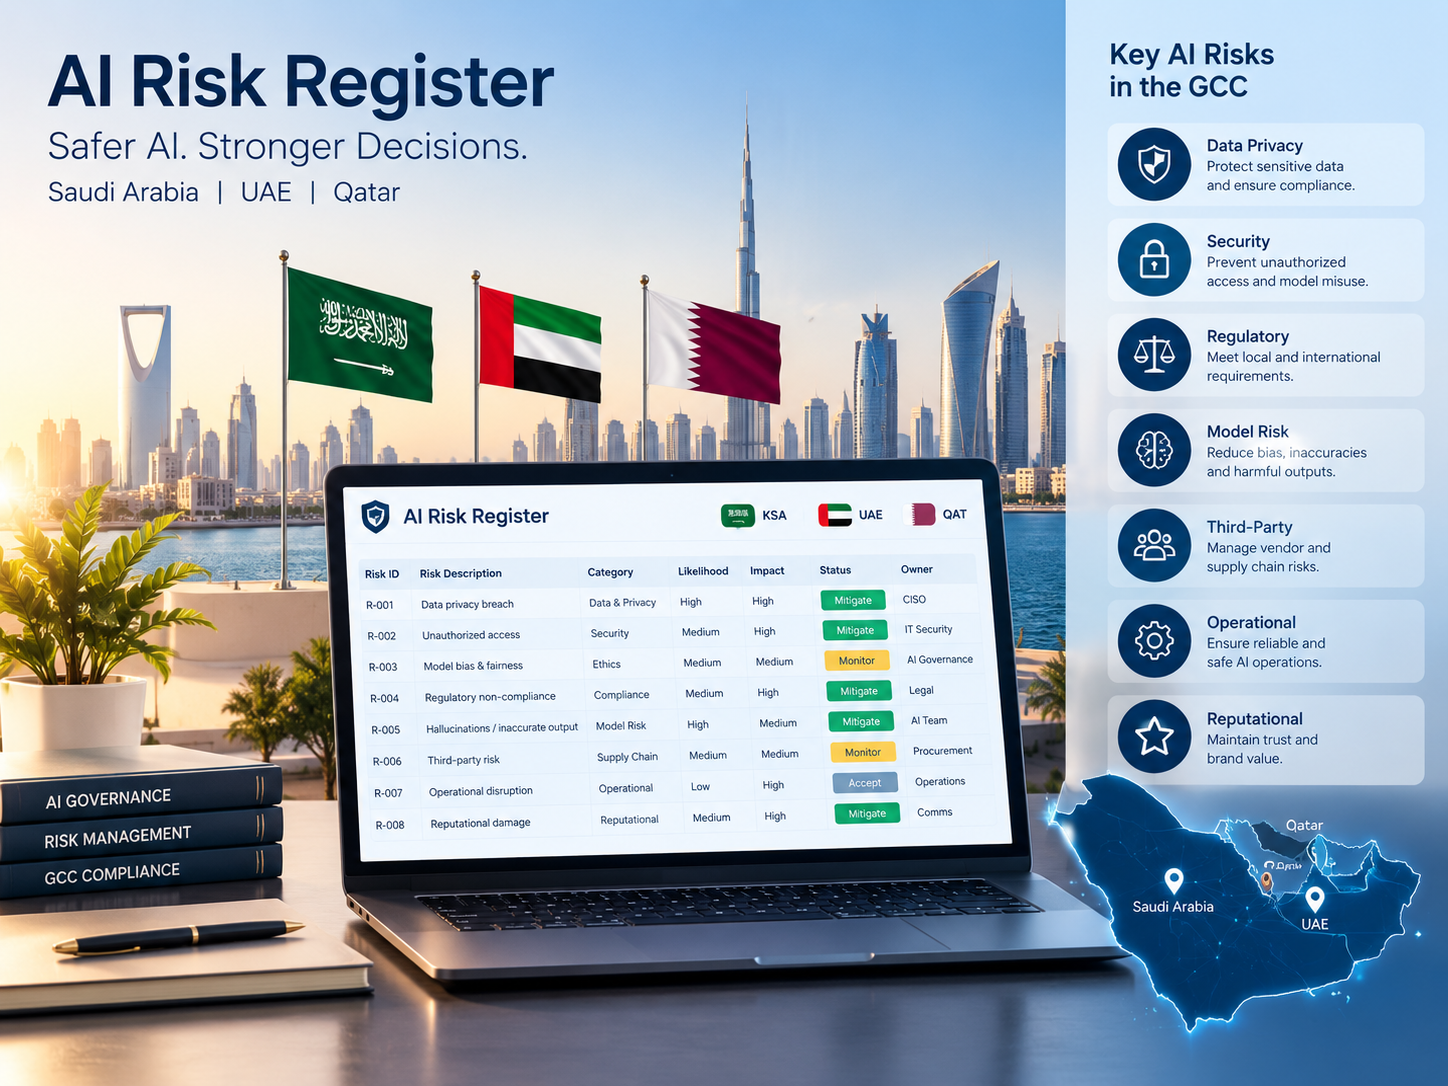
An AI risk register is a living governance record that helps organizations identify AI risks, assess their likelihood and impact, assign accountable owners, document controls and monitor residual exposure. For GCC businesses, it should also reflect applicable privacy, cybersecurity, model-governance and human-oversight requirements in Saudi Arabia, the UAE and Qatar.
Why GCC Companies Need an AI Risk Register
AI adoption across Riyadh, Dubai, Abu Dhabi and Doha is moving quickly. Generative AI, automated decision-making and third-party models can improve efficiency and customer experiences, but they also introduce risks around privacy, bias, cybersecurity, hallucinations, data leakage and vendor dependency.
An AI risk register gives teams one structured place to record those exposures and decide how they will be controlled, monitored and escalated.
For businesses developing digital platforms through custom web development services or mobile application development, the register can become part of the wider product and AI lifecycle rather than a separate compliance exercise.
What Is an AI Risk Register?
An AI risk register records identifiable risks associated with AI systems throughout their lifecycle.
Unlike a general enterprise risk register, it captures AI-specific concerns such as model bias, explain ability, hallucinations, training and input data, human oversight, model updates and third-party dependencies. It is also different from an AI inventory: an inventory tells you which AI systems exist, while a risk register focuses on what could go wrong and how those risks are managed.
What Should an AI Risk Register Contain?
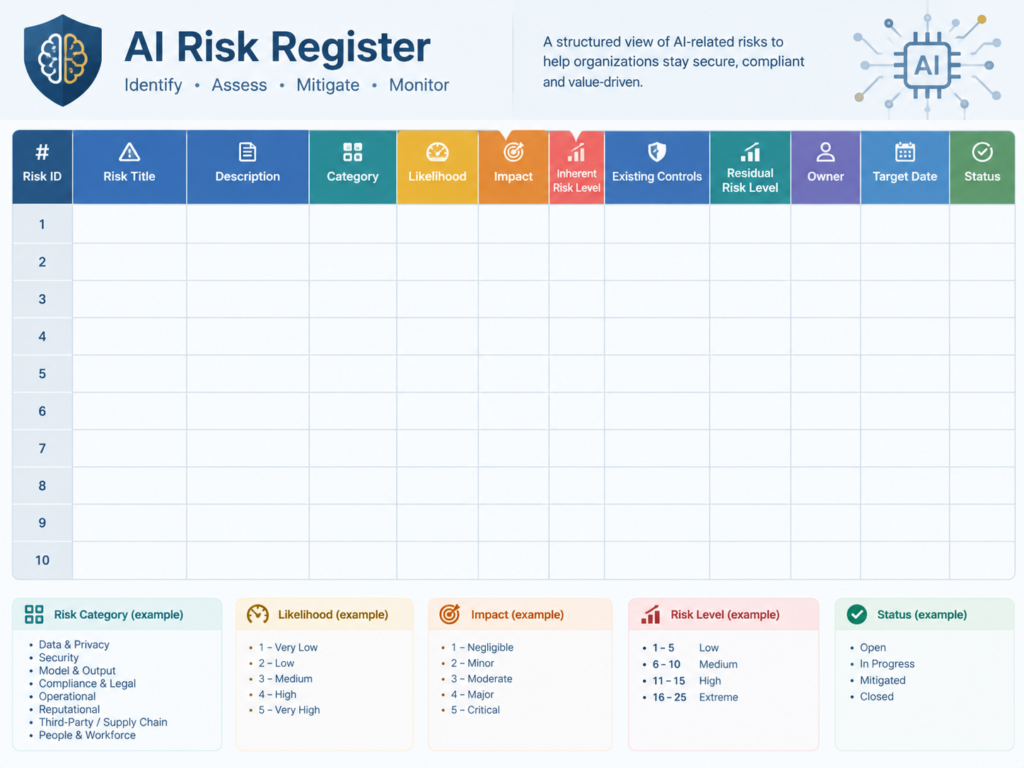
A practical register will usually capture.
AI system and business use case
Risk category and description
Affected stakeholders
Likelihood and impact
Inherent risk score
Existing controls
Risk and action owners
Mitigation actions
Residual risk
Monitoring indicators
Review date and reassessment triggers
Supporting evidence
For Saudi, UAE and Qatar organizations, these fields help connect AI governance with privacy, cybersecurity, vendor management and responsible AI practices.
How to Build an AI Risk Register Step by Step
How do you build an AI risk register for a GCC company? Start by identifying the AI systems your organization uses, document the risks associated with each system, score those risks consistently, and assign controls and accountable owners. Then monitor residual exposure and reassess whenever the model, data, vendor, use case or regulatory environment changes.
Inventory AI Systems and Use Cases
Start with visibility. Record internal models, generative AI assistants, third-party AI platforms, customer-facing systems and automated decision-making tools.
The inventory should describe what each system does, what data it uses, who interacts with it and which business process depends on its output.
For example, a Riyadh fintech might include fraud-detection models, while a Dubai retailer could document recommendation engines integrated into its e-commerce platform. Logistics companies may need to capture forecasting, optimization and routing models.
Identify and Score AI Risks
Once the systems are mapped, identify credible risks for each use case.
A simple likelihood × impact methodology can work well, provided the scoring criteria are clearly defined and applied consistently.
Common areas to assess include.
Privacy and personal-data exposure
Cybersecurity threats
Bias and discrimination
Hallucinated or inaccurate outputs
Explain ability
Arabic-language accuracy
Confidential-data leakage
Intellectual-property exposure
Vendor dependency
Model or service failure
Inadequate human oversight
The score should reflect the organization’s actual context. The same AI failure can have very different consequences in a marketing workflow and a financial decision-making process.
Assign Controls, Owners and Review Dates
Every material risk needs clear accountability.
Document preventive and detective controls, the person responsible for the risk, required mitigation actions, deadlines, residual exposure and the events that should trigger reassessment.
A simplified entry might look like this.
| AI risk | Likelihood | Impact | Control | Owner | Residual risk |
|---|---|---|---|---|---|
| Arabic chatbot provides inaccurate financial guidance | 3 | 5 | Pre-release testing and human escalation | Product/Risk | Medium |
Scoring scales should be defined internally so that teams understand what each likelihood and impact value means.
GCC AI Risk Register Template.
A useful AI risk register template should do more than list technical problems. It should connect each risk to its business consequences, controls, ownership and evidence.
Risk Identification and Classification
Capture the risk ID, business unit, AI system, use case, relevant data sources, risk category, affected stakeholders and a concise risk statement.
A good risk statement should make the cause, event and potential consequence understandable without requiring specialist AI knowledge.
Risk Scoring, Controls and Residual Risk
Add fields for likelihood, impact, inherent risk, existing controls, control effectiveness, residual risk and risk tolerance.
Organizations developing AI-enabled portals through React development services should connect technical safeguards with business risks rather than maintaining governance as disconnected documentation.
Ownership, Monitoring and Evidence
The register should also capture.
Risk owner
Action owner
Risk treatment
Mitigation deadline
Current status
KRI or KPI
Review date
Supporting evidence
Escalation requirements
A spreadsheet can be enough when an organization is starting out. As the number and complexity of AI systems grow, the same methodology can be integrated into broader GRC or business-intelligence workflows.
Saudi Arabia, UAE and Qatar AI Governance Considerations
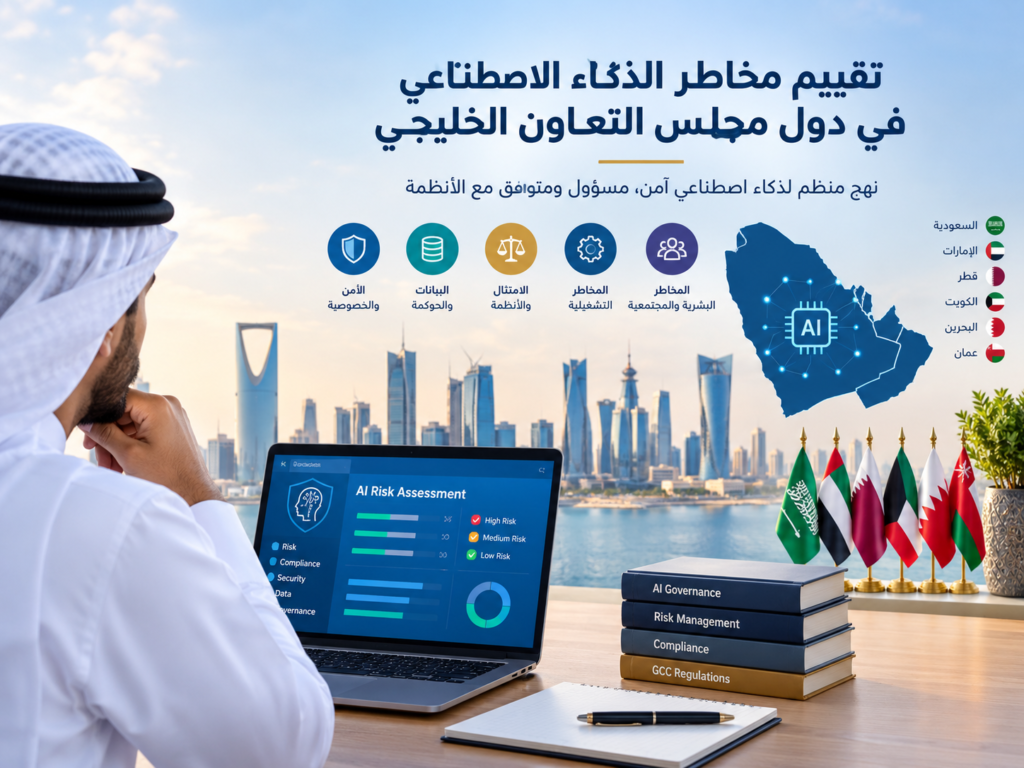
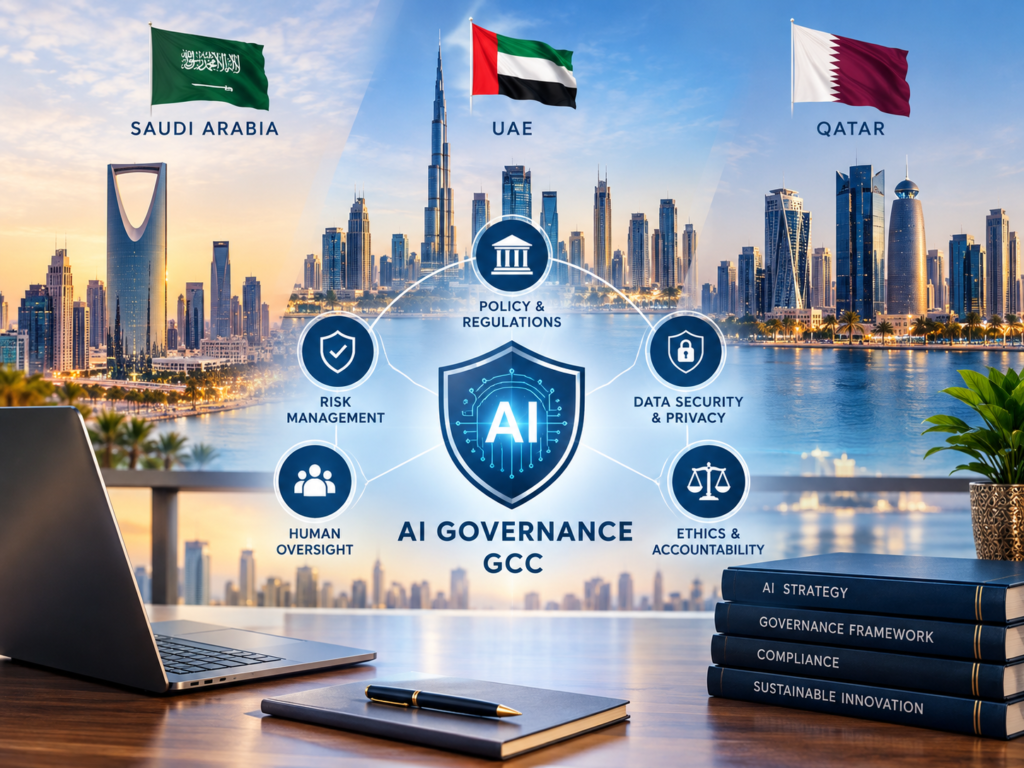
AI risks should not automatically be treated the same way across Saudi Arabia, the UAE and Qatar. Organizations can use a common register structure, but regulatory references, risk appetite, controls and evidence requirements should reflect the jurisdiction, sector, data and use case involved.
Saudi Arabia.
Saudi organizations should consider relevant SDAIA AI-governance guidance alongside applicable data-management and personal-data requirements.
Privacy, security, reliability, explain ability and risk management can therefore become explicit categories or control areas within the register.
For financial-services organizations, SAMA requirements may also be relevant. SAMA should be considered in the context of regulated financial activities rather than treated as Saudi Arabia’s general AI regulator.
UAE.
UAE businesses need to distinguish between federal, free-zone and sector-specific requirements.
For regulated financial institutions, model governance, validation, monitoring and controlled model use may require additional documentation and evidence. TDRA, ADGM and DIFC requirements or guidance can also become relevant depending on the organization’s location, activities and regulatory status.
A Dubai commerce company scaling through WooCommerce development, for example, may want separate register entries for customer-data exposure, third-party AI services and automated personalization.
Qatar.
Qatar organizations should similarly map AI risks to the requirements that actually apply to their sector.
For QCB-regulated entities, governance areas such as risk assessment, security, bias, transparency and accountability may need to be reflected in AI-risk documentation. A Doha financial institution can connect its AI register to established enterprise risk processes, while organizations outside QCB supervision should identify their own applicable regulatory and sector obligations.
AI Risks GCC Companies Should Track
The exact register will vary by organization, but several risk categories deserve particular attention across GCC markets.
Privacy, Cybersecurity and Data Residency
Track sensitive information entered into AI prompts, unauthorized access, cross-border data transfers, third-party processors and unintended exposure of training or operational data.
Regional hosting can support an organization’s data strategy, but hosting location alone does not establish regulatory compliance. Data classification, access controls, contractual arrangements and applicable transfer requirements still matter.
Bias, Arabic AI Performance and Explain ability
Arabic-language performance deserves explicit testing when AI is used with GCC customers or employees.
Models may behave differently across Modern Standard Arabic, regional dialects, bilingual Arabic-English conversations and transliterated text. Those differences can create accuracy, fairness, operational and customer-experience risks.
Testing should therefore reflect the language people actually use rather than relying only on generic English-language benchmarks.
Vendor, Generative AI and Human-Oversight Risks
Third-party and generative AI introduce their own risk profile.
Important issues include foundation-model changes, vendor dependency, prompt leakage, intellectual-property exposure, hallucinated outputs, service interruptions and inadequate human review.
Organizations creating AI-powered customer interfaces through professional web design services should consider escalation and human-review paths as part of the user experience, particularly where inaccurate output could have significant consequences.
How to Maintain an AI Risk Register
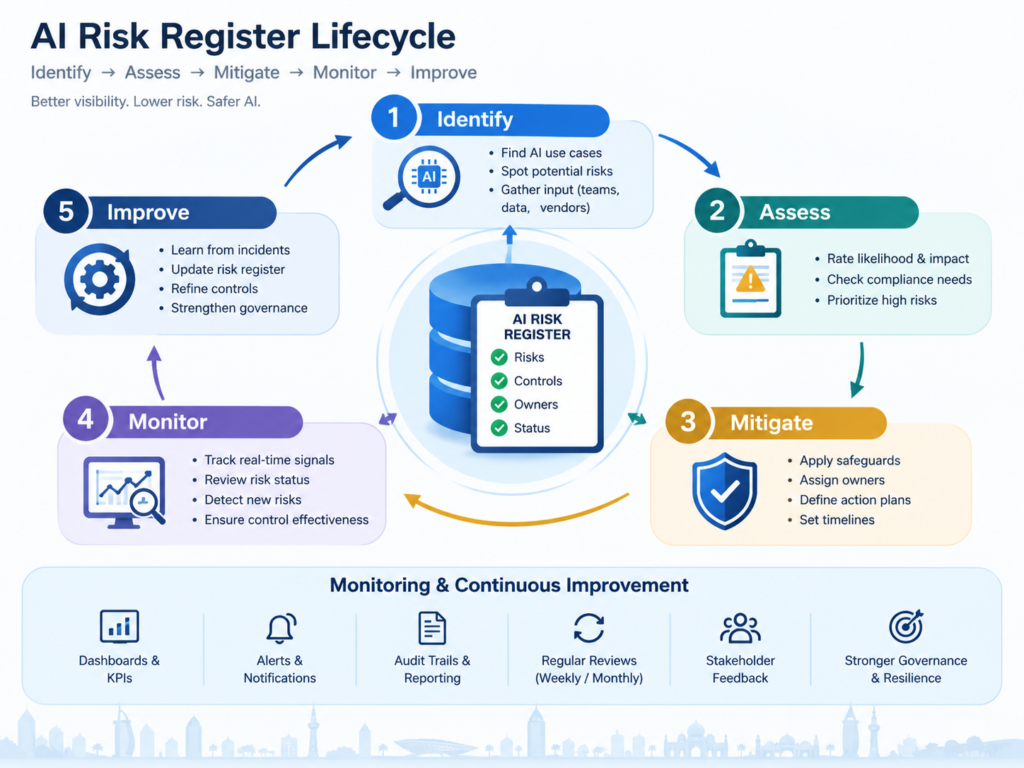
Creating the register is only the beginning. Its value comes from keeping it connected to operational decisions.
Set Clear Risk Owners and Review Frequencies
Business owners should remain accountable for business consequences, while technical, cybersecurity, privacy, legal and compliance specialists can own or support the controls relevant to their areas.
Higher-risk AI systems generally justify closer monitoring and more frequent reassessment than low-impact internal tools.
Define Reassessment Triggers
Do not rely only on calendar-based reviews. Reassess an AI risk when there is a meaningful change, such as.
A new model or major model update
A new dataset or data source
An AI-related incident
A change of vendor
Material performance deterioration
A regulatory or policy change
Expansion into another GCC jurisdiction
A significant change in the AI use case
Connect the Register to Wider AI Governance
Link the register with the organization’s AI inventory, incident-management processes, vendor assessments, cybersecurity controls, privacy reviews, internal audit and management reporting.
That connection turns the AI risk register from a static spreadsheet into an operational responsible-AI control.
Last Words
An effective AI risk register does not need to be complicated. It needs to be consistent, owned and regularly updated.
For GCC organizations, the strongest approach is usually to maintain a common risk methodology while mapping controls and evidence to the specific requirements of Saudi Arabia, the UAE or Qatar. Arabic-language performance, third-party AI, data handling and human oversight also deserve explicit attention rather than being buried inside broad technology-risk categories. ( Click Here’s )
Need an AI risk register tailored to your GCC technology environment? Explore Mak It Solutions’ technology services or contact the team to discuss a Saudi, UAE or Qatar digital strategy built around practical governance and scalable systems.
FAQs
Q : How often should Saudi companies update an AI risk register?
A : There is no single review interval that suits every Saudi organization. Higher-risk systems can be reviewed more frequently, with additional event-driven assessments after significant changes to models, data, vendors, use cases, incidents or applicable requirements.
Q : Does a UAE company need a separate risk register for generative AI?
A : Not necessarily. A UAE organization can maintain one enterprise AI risk register while classifying generative-AI risks separately. This keeps governance centralized while still documenting risks such as hallucination, prompt leakage, intellectual-property exposure, privacy, vendor dependency and inadequate human oversight.
Q : Which AI risks should Qatar financial institutions document?
A : Relevant risks can include bias, privacy, cybersecurity, transparency, accountability and operational exposure. Regulated organizations should connect individual AI systems and their risks with applicable requirements, controls, owners, monitoring and the institution’s wider risk-management framework.
Q : Should GCC companies include Arabic-language AI risks in their register?
A : Yes, whenever Arabic is used in customer, employee or automated workflows. Testing should consider Modern Standard Arabic, relevant dialects, bilingual interactions, transliteration, translation inconsistencies, hallucinations and material differences in model performance.
Q : Can one AI risk register template be used across GCC countries?
A : Yes, a common AI risk register template can provide baseline fields, scoring criteria and governance workflows. Organizations should then customize regulatory mappings, controls, evidence and data-handling requirements for each jurisdiction and sector rather than assuming that one implementation automatically satisfies every GCC requirement.