AI Agent Credentials: Why Short-Lived Access Wins
AI Agent Credentials: Why Short-Lived Access Wins
AI Agent Credentials: Why Short-Lived Access Wins
AI agents are changing how enterprise access works. Unlike traditional applications with predictable identities and fixed service accounts, autonomous agents may be created dynamically, call several APIs, act on behalf of users, delegate work to other agents, and disappear minutes later.
That makes AI agent credentials an identity and security architecture problem, not simply another secrets-management issue. In most enterprise environments, the safer approach is to give agents short-lived, narrowly scoped credentials tied to a specific identity, task, audience, resource, and user context rather than handing them reusable static secrets.
For a broader identity foundation, see Mak It Solutions’ AI Agent Identity Management Guide.
What Are AI Agent Credentials?
AI agent credentials are the keys, tokens, certificates, or other cryptographic proofs an autonomous agent uses to authenticate itself and access systems.
A well-designed credential should answer four questions.
Which agent is presenting it?
What resource can the agent access?
What action is the agent allowed to perform?
How long should that authority remain valid?
Modern architectures increasingly make these credentials temporary, identity-bound, audience-restricted, and specific to the task being performed.
AI Agent Credentials vs. AI Agent Authentication
A credential is what the agent presents. Authentication is the process used to verify the identity or workload behind that credential.
An OAuth access token, for example, is a credential. Checking its issuer, signature, audience, expiry, and associated workload identity is part of the authentication process.
AI Agent Identity vs. Workload Identity
An AI agent identity represents the autonomous software actor itself. Workload identity is the broader mechanism used to identify non-human workloads such as applications, containers, functions, services, and processes.
AI agents often need more granular lifecycle controls because their authority may exist only for one workflow, delegated action, or session.
NIST has highlighted the need to treat AI agents as identifiable entities with their own credentials and entitlements rather than simply allowing them to reuse human credentials.
Mak It Solutions explores this wider model in its AI Agent Identity Security Guide.
Common Credential Types for AI Agents
Organizations may use
Static API keys
OAuth access tokens
JSON Web Tokens (JWTs)
X.509 certificates
Cloud service-account credentials
Temporary cloud credentials
Federated workload identities
The format matters less than the security properties around it: lifetime, identity, scope, audience, revocation, and permitted resources.
Why Short-Lived AI Agent Credentials Matter
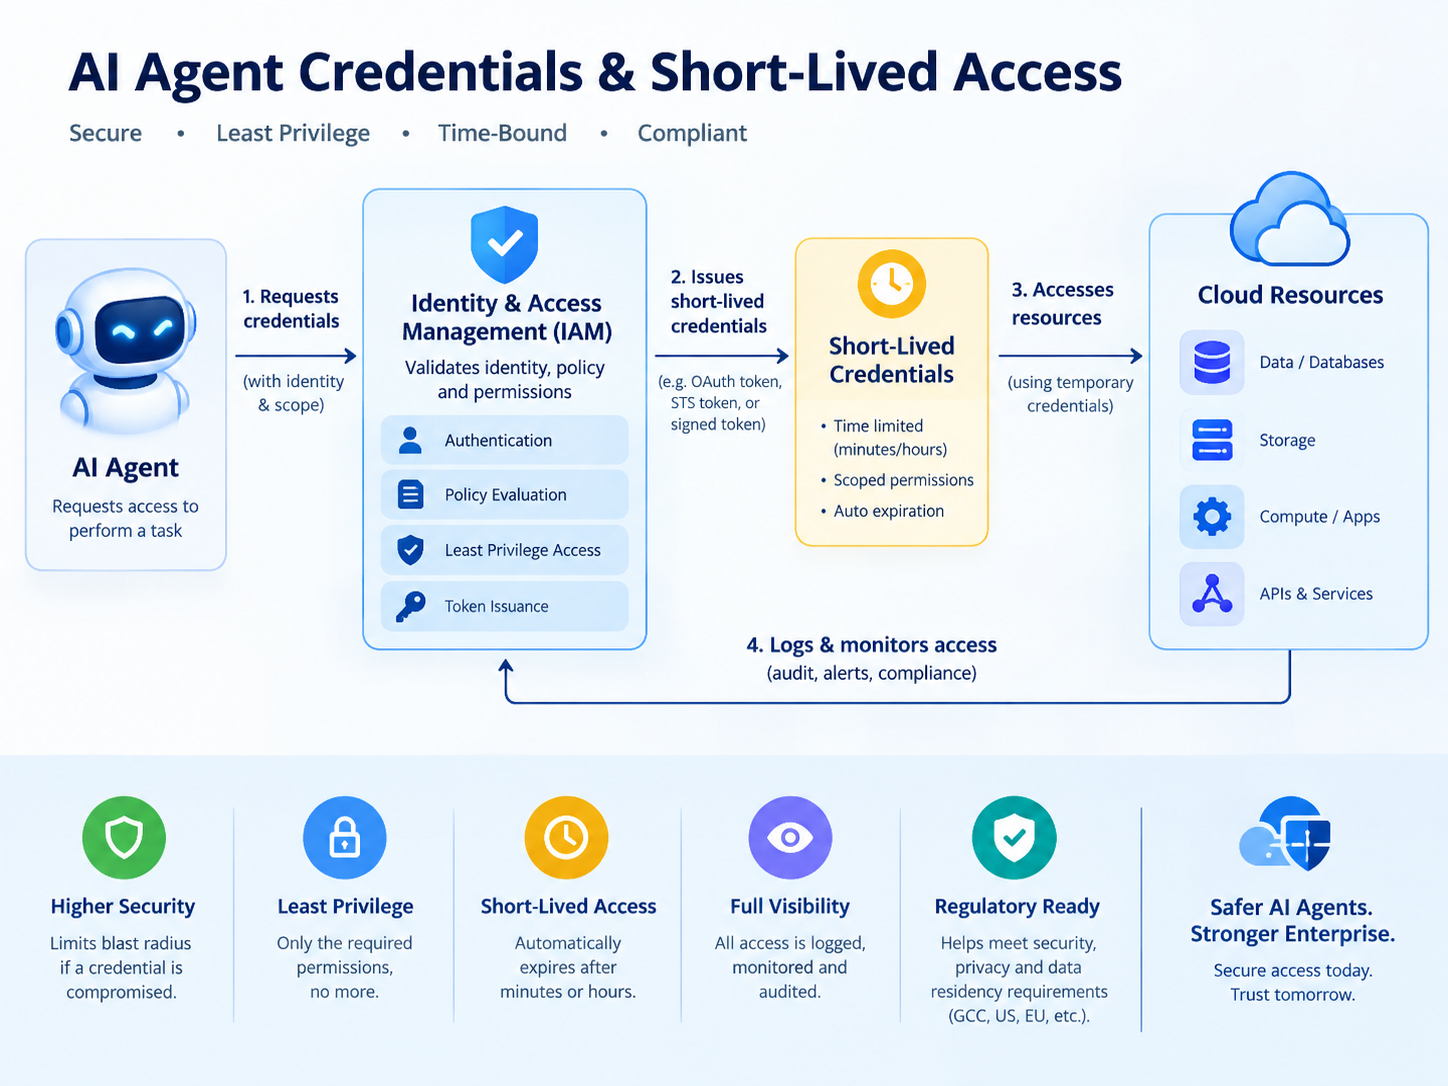
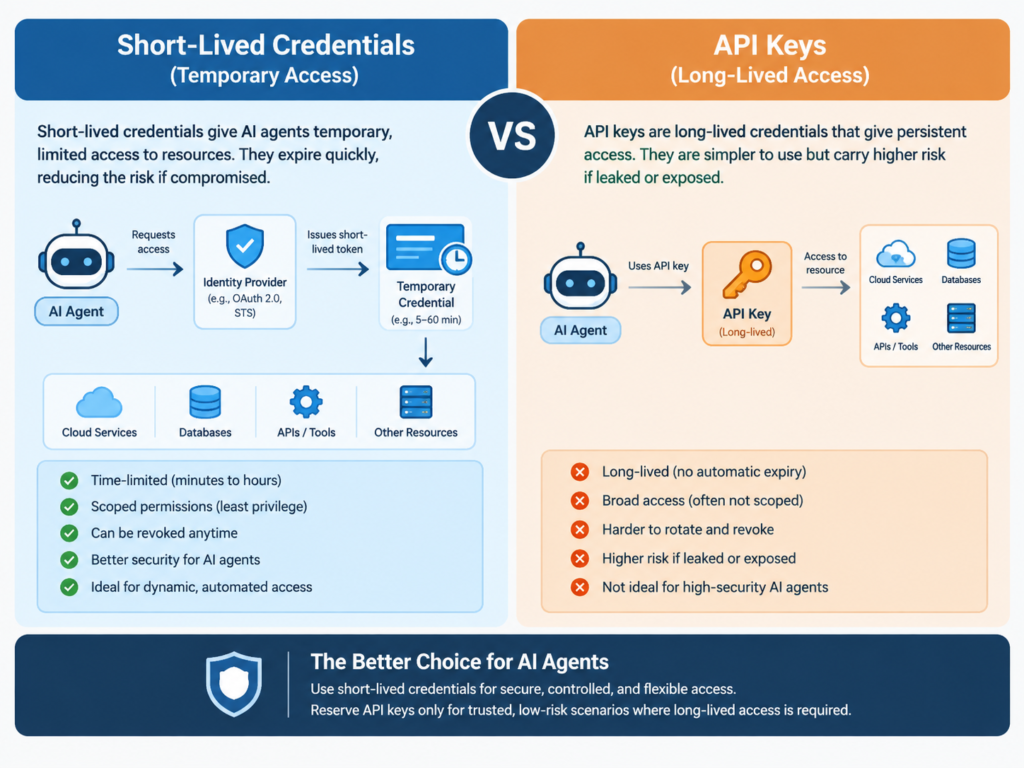
Short-lived credentials reduce the period during which a compromised agent or stolen token can be abused.
Instead of storing a reusable secret, the agent receives temporary authority that expires after a task, session, or tightly defined access window.
This is particularly important for autonomous systems because agents can move across tools and APIs at machine speed. A persistent credential that leaks into a log, prompt, repository, debugging session, or downstream workflow can remain useful long after the original task has ended.
The Risk of Static API Keys and Persistent Secrets
Static API keys are simple to deploy, but they often create broad and long-lasting access.
Common problems include.
Keys copied into source code or configuration files
Secrets exposed in logs or debugging tools
Shared credentials that make attribution difficult
Broad permissions accumulated over time
Manual rotation that rarely happens often enough
Credentials remaining valid after the original workload disappears
NIST has also warned about the identity, replay, revocation, and access-control limitations associated with persistent bearer-style credentials in agentic environments.
How Ephemeral Credentials Reduce Blast Radius
Consider the difference between a credential valid for months and one valid for only a few minutes.
Both can theoretically be stolen. But the shorter-lived credential gives an attacker less time to exploit it.
A strong ephemeral credential may also be restricted to.
One API
One workload
One resource
One task
One user delegation
One specific audience
Short expiration does not eliminate risk. It limits standing privilege and reduces how useful a stolen credential remains.
Task-Scoped Credentials for Autonomous Workflows
Authority should follow the task.
An invoice-processing agent, for example, might receive temporary permission to read one approved storage location and create one transaction in an ERP system. It does not need a permanent finance service account with broad access to every related system.
The same principle applies to agent-to-agent delegation. A downstream agent should receive only the authority required for its portion of the workflow, not every permission held by the original agent.
How AI Agent Authentication Should Work
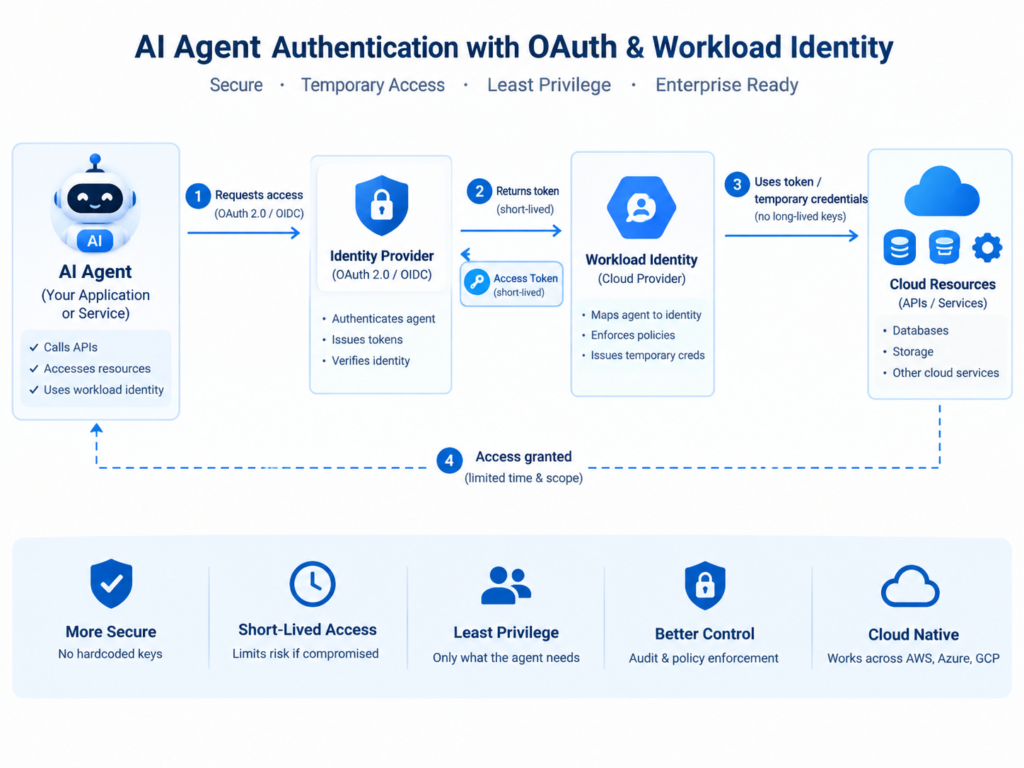
A secure AI agent authentication flow typically starts by verifying the workload itself. Only then should the system issue a short-lived credential containing the permissions, resource restrictions, delegated context, and audience needed for the current task.
Workload Identity, Federation, and Credential Brokers
A workload identity platform or credential broker can verify runtime signals and issue temporary credentials without embedding a permanent secret inside the agent.
This may include signals such as.
Workload identity
Runtime environment
Cloud account or tenant
Device or execution context
Requested resource
Delegated human identity
Current policy state
Federation extends this model across cloud providers and security domains, making it useful for distributed SaaS platforms and systems built through secure back-end development services.
OAuth, Token Exchange, DPoP, and mTLS
OAuth provides a strong foundation for delegated authorization.
IETF RFC 8693 defines OAuth 2.0 Token Exchange, allowing one token to be exchanged for another token that is appropriate for a different resource, audience, or delegated workflow.
This is especially useful when one AI agent needs to call another service without forwarding its original broad authority unchanged.
DPoP adds proof-of-possession characteristics to OAuth tokens, while mutual TLS can bind access to cryptographic certificates. Both approaches can reduce the usefulness of a stolen bearer token.
SPIFFE/SPIRE and Cloud-Native Agent Identity
SPIFFE provides workload identities through short-lived X.509 or JWT-based identity documents. SPIRE can automate workload attestation and credential issuance without requiring workloads to begin with a manually provisioned secret.
Similar principles appear across major cloud identity systems, including temporary role credentials, managed identities, workload federation, and emerging agent-identity platforms.
The architectural goal is consistent: establish workload identity first, then issue limited authority dynamically.
Apply Least Privilege and Zero Trust to AI Agent Access
Least privilege means giving an agent only the authority it needs for its current action. Zero Trust adds continuous verification instead of assuming that an authenticated agent should remain trusted indefinitely.
For AI agent credentials, these two principles should work together.
Mak It Solutions covers the wider architecture in its Zero Trust Strategy for AI-Era Security.
Bind Access to Agent, User, Resource, and Task
A useful authorization policy should establish.
Which agent is acting?
Who or what authorized the agent?
Which resource does it need?
What action is it performing?
Why is that action required?
How long should the access remain valid?
That is far more useful than a generic shared API key that provides no meaningful task or actor context.
Delegated Authorization Without Permanent User Impersonation
When an AI agent acts for a user, the architecture should preserve the distinction between the user and the agent wherever possible.
RFC 8693 supports actor context and distinguishes delegation from simple impersonation.
This matters because an agent should not silently become an unrestricted, permanent copy of a user’s authority. The system should know both who authorized the action and which non-human identity actually executed it.
Revocation, Rotation, and Auditability
Short-lived credentials reduce dependence on manual rotation, but they do not remove the need for revocation controls.
Security teams should still be able to.
Disable an agent identity
Terminate delegated authority
Revoke refresh tokens or sessions
Change access policy immediately
Block access at an API gateway
Investigate complete audit trails
Continuous telemetry is equally important. Mak It Solutions’ AI Security Monitoring Guide covers logging and monitoring patterns in greater depth.
AI Agent Credential Management Across the USA, UK, Germany, and EU
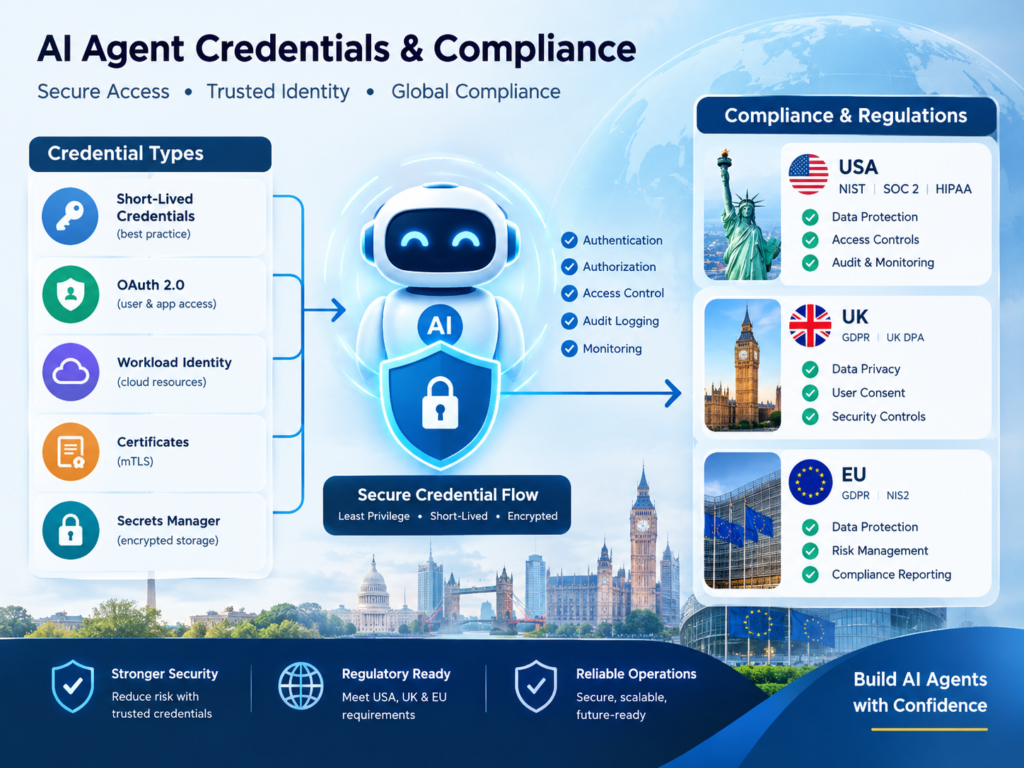
Regulations do not generally prescribe one universal token lifetime for AI agents. However, requirements around security, accountability, auditability, data protection, and access control strongly support well-governed machine identity.
USA.
For AI agent credentials in the USA, NIST Zero Trust guidance provides a useful architectural baseline.
Healthcare organizations must also consider HIPAA requirements where agents access electronic protected health information. Relevant controls include access management, audit capabilities, authentication, and transmission security.
For a SaaS platform operating in markets such as New York or San Francisco, that means connecting AI agent identity with cloud IAM, policy enforcement, monitoring, and least privilege rather than allowing autonomous systems to inherit a shared administrator account.
SOC 2 environments may also benefit from this model because unique identities and well-defined access paths make control ownership and audit evidence easier to establish.
UK.
For AI agent authentication in the UK, organizations processing personal data should consider UK GDPR accountability and data protection by design.
The ICO emphasizes appropriate technical and organizational safeguards throughout the data-processing lifecycle.
In financial services, NHS-related systems, or other regulated environments, purpose-bound access and strong auditability become particularly important when agents interact with sensitive information or external APIs.
A short-lived credential does not itself make a system compliant, but it can support cleaner access control, accountability, and containment.
Germany and EU.
For KI-Agent Zugangsdaten Deutschland, a practical architecture combines kurzlebige Zugangsdaten für KI-Agenten with strong attribution, controlled delegation, and policy enforcement.
GDPR/DSGVO principles such as security, accountability, data minimization, and purpose limitation can make broad reusable credentials harder to justify for sensitive workflows.
NIS2 and DORA introduce additional cybersecurity and operational-resilience expectations for organizations within their respective scopes.
For financial institutions in Frankfurt, SaaS providers in Berlin, or other organizations processing cross-border EU data, workload identity EU architectures can provide clearer separation between human and machine authority while improving auditability.
Short-Lived Credentials vs. API Keys for AI Agents
Short-lived credentials generally provide more granular control than persistent API keys, although they require stronger identity infrastructure.
| Credential Type | Typical Lifetime | Scope | Identity Context | Revocation Model | Best Fit | Main Risk |
|---|---|---|---|---|---|---|
| Static API key | Long | Often broad | Limited | Manual rotation | Simple integrations | Leakage and reuse |
| OAuth token | Short to medium | Granular | User or workload context | Policy, expiry, or revocation | Delegated API access | Bearer-token theft |
| X.509 workload credential | Short | Policy-based | Strong workload identity | Automated renewal | Service-to-service access | PKI complexity |
| Cloud STS token | Short | Role or policy based | Cloud workload context | Expiry and policy | Cloud-native agents | Misconfigured roles |
Security and Credential Lifetime
A persistent API key creates standing access. A short-lived token reduces that exposure window.
The right lifetime depends on operational requirements and risk, but the design principle is simple: credentials should not remain valid longer than the job requires.
Scope, Delegation, and Identity Context
Modern authorization tokens can include.
Scopes
Audiences
Resource restrictions
User delegation
Actor identity
Expiry
Policy context
A basic API key usually provides far less context.
Operational Trade-Offs
Ephemeral access requires supporting infrastructure.
Organizations may need.
Identity providers
Security Token Services
Credential brokers
Federation
Policy engines
High-availability token issuance
Centralized logging
Revocation controls
That adds architectural complexity, but it replaces hidden credential sprawl with managed identity infrastructure.
Best Practices for AI Agent Credential Management
Organizations implementing AI agent credentials should focus on a few practical controls.
Eliminate Embedded and Shared Agent Secrets
Avoid hard-coding credentials in.
Prompts
Source code
Agent configuration
Containers
Build pipelines
Repositories
Shared service accounts should also be avoided when the platform can support unique workload identities.
Make Short-Lived Credentials the Default
Use federation, cloud STS services, credential brokers, managed identities, SPIFFE/SPIRE, or dynamic secrets wherever practical.
Credential issuance should evaluate factors such as:
Agent identity
Execution environment
Requested resource
User delegation
Risk signals
Task context
Required scope
Teams modernizing their wider infrastructure can connect this work with Mak It Solutions’ services portfolio and Business Intelligence Services.
Keep Credentials Narrowly Scoped
Do not issue a broad credential simply because an agent may eventually need several tools.
Prefer a sequence of smaller authorization decisions.
For example, an agent may receive one token to read a customer record and a separate token to call a billing API. Each credential can then have its own audience, scope, policy, and expiry.
Preserve Delegated User Context
When an agent acts for a person, retain both identities in logs and authorization decisions.
Security teams should be able to answer.
Which human authorized the activity?
Which agent performed it?
Which credential was used?
Which resource was accessed?
Which policy permitted the action?
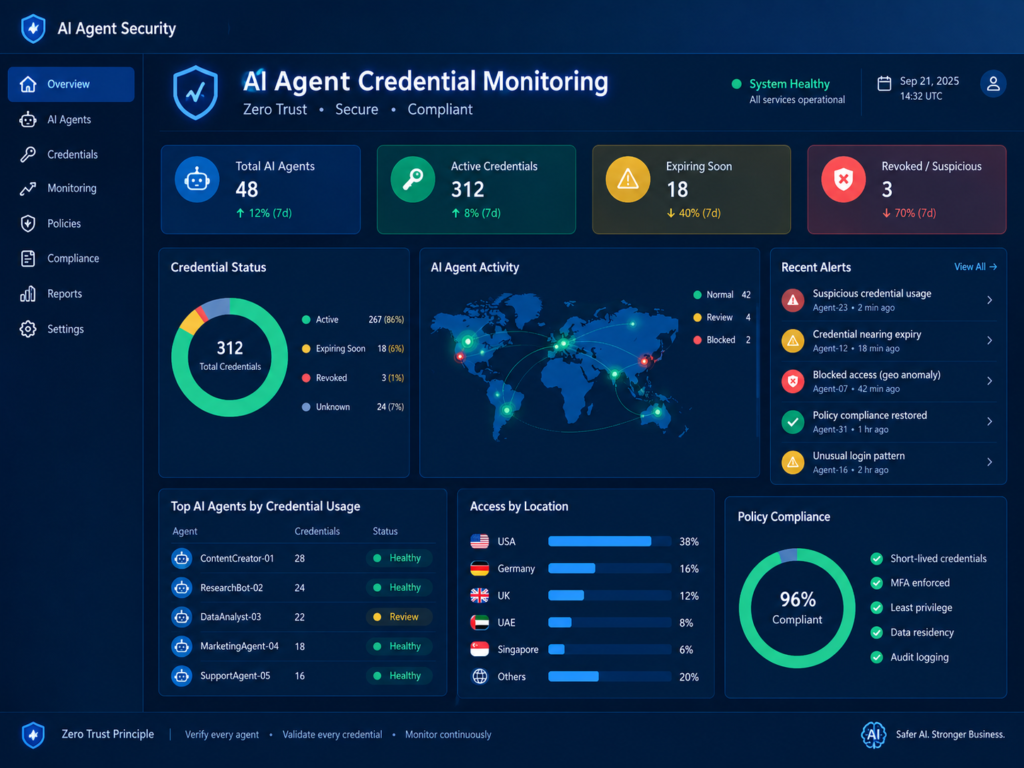
Monitor Agent Actions and Credential Use Continuously
Logs should capture enough information to reconstruct the authorization chain.
Useful events include.
Agent identity
Human or system owner
Delegated user context
Credential issuer
Requested resource
Audience
Scope
Issue time
Expiry
Token exchange
API call
Policy decision
Revocation event
Source environment
Security teams should also watch for unexpected delegation chains, unusual cross-cloud activity, repeated token failures, abnormal resource access, and unexplained agent-to-agent credential use.
Concluding Remarks
As autonomous systems gain access to more APIs, SaaS platforms, cloud services, and sensitive data, persistent secrets become increasingly difficult to justify.
A stronger model gives every agent a clear identity and issues AI agent credentials dynamically, with short lifetimes, narrow scopes, explicit audiences, and complete audit trails.
If your organization is already deploying AI agents, now is a useful time to identify persistent secrets, shared service accounts, excessive permissions, and weak delegation paths. Explore Mak It Solutions’ technology services or request a scoped consultation to plan a practical migration toward short-lived, identity-based access.
Key Takeaways
Strong AI agent credential management is less about choosing one token format and more about controlling identity, authority, lifetime, and context.
Organizations should:
Give AI agents unique identities rather than shared human credentials
Prefer short-lived, task-scoped access over persistent API keys
Bind authority to the agent, user context, audience, resource, and task
Use workload identity, federation, OAuth token exchange, SPIFFE/SPIRE, or cloud STS where appropriate
Apply least privilege and Zero Trust throughout agent workflows
Maintain rapid revocation, monitoring, and audit logging
Map identity controls to applicable regulatory requirements in the USA, UK, Germany, and EU
The key principle is straightforward: AI agent credentials should provide the minimum authority required for the minimum time required.
FAQs
Q : How long should an AI agent credential remain valid?
A : There is no universal lifetime. Ideally, the credential should remain valid only as long as the task or session requires, with enough operational tolerance to avoid unnecessary failures. Higher-risk actions may justify very short lifetimes, while other workloads may need longer windows.
Q : Can AI agents safely share service accounts?
A : They can, but shared accounts weaken attribution, lifecycle control, and least privilege. Where possible, give each agent or workload its own identity and issue temporary credentials based on policy. If shared accounts cannot yet be removed, restrict their permissions and monitor them closely.
Q : How can enterprises revoke an AI agent’s access immediately?
A : An organization can disable the agent identity, revoke a refresh token or session, change authorization policy, terminate delegated authority, or block the workload through an API gateway or enforcement point. Short token lifetimes add another layer of containment because existing credentials expire automatically.
Q : Do AI agents need a separate identity for every task or session?
A : Not necessarily. A persistent logical agent can keep one stable identity while receiving different short-lived credentials for individual workflows. Highly sensitive environments may choose per-session or per-task identities for stronger isolation.
Q : What should security teams log when AI agents use credentials?
A : Logs should record the agent identity, delegated user context, credential issuer, resource, scope, audience, issue and expiry information, policy decision, API action, token exchange, and revocation events. The goal is to make every significant autonomous action attributable and reviewable.