AI Governance Committee: A Practical GCC Guide
AI Governance Committee: A Practical GCC Guide
AI Governance Committee: A Practical GCC Guide
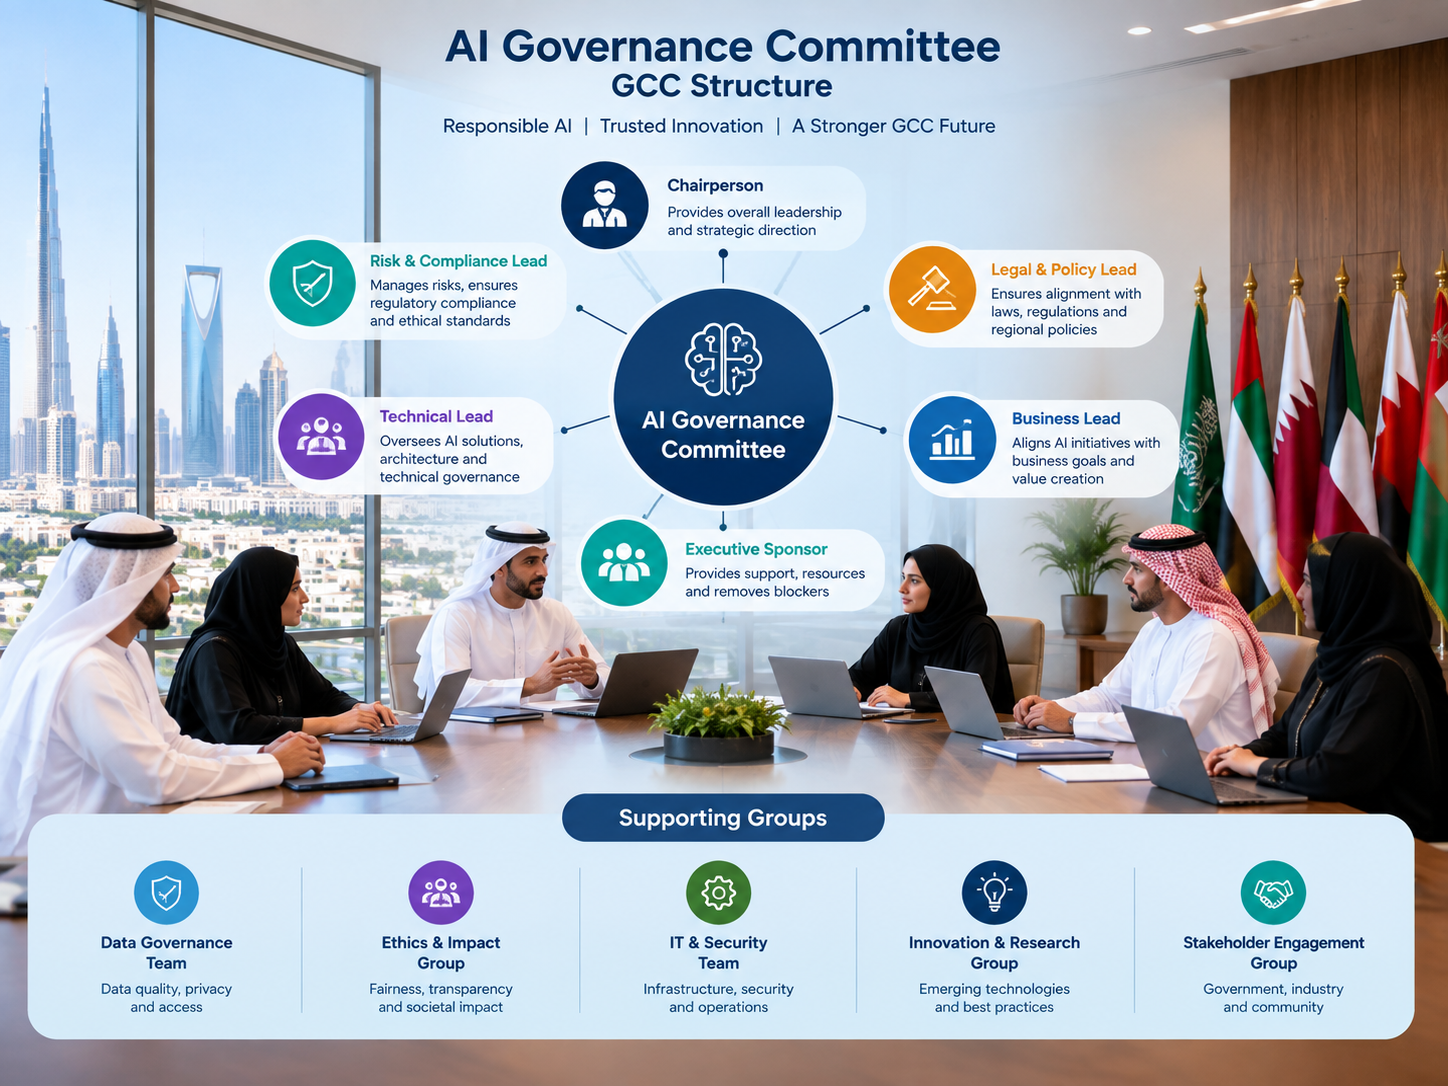
An AI governance committee gives GCC organizations a formal way to decide how AI systems are approved, monitored, controlled, and escalated. For enterprises in Saudi Arabia, the UAE, and Qatar, the committee connects responsible AI with privacy, cybersecurity, data governance, vendor management, and regulatory accountability.
As AI adoption accelerates across Riyadh, Dubai, Abu Dhabi, Doha, and Jeddah, that oversight is becoming harder to treat as optional. Employees may already be using generative AI tools, SaaS platforms may introduce AI features without much visibility, and business teams may launch pilots before governance teams know they exist. The result is often shadow AI—AI use that sits outside formal approval and monitoring processes.
What Is an AI Governance Committee?
An AI governance committee is a cross-functional enterprise oversight body responsible for making and documenting decisions about material AI use cases.
It is not an AI development team. Its role is to establish governance expectations, challenge proposed deployments, allocate risk ownership, approve or escalate higher-risk systems, and monitor exceptions after approval.
AI Governance Committee vs. AI Governance Framework
The terms are related, but they are not interchangeable.
An AI governance framework is the broader system of policies, inventories, risk classifications, monitoring requirements, technical controls, evidence, and reporting.
The AI governance committee is the decision-making body operating within that framework.
Mak It Solutions’ AI governance policy GCC guide explains how governance policies and controls can be translated into practical enterprise processes across the region.
Why a Policy Alone Is Not Enough
A written policy can define principles, but it cannot resolve every real-world decision involving sensitive data, third-party AI, automated decision-making, human oversight, or exceptions.
Organizations still need clearly assigned people with authority to answer questions such as.
Can this AI system go live?
Does it require additional privacy or security review?
Is human approval mandatory?
Can the vendor process confidential information?
Who accepts the remaining risk?
What happens if the system changes after approval?
A committee turns governance principles into accountable decisions.
Who Should Sit on an AI Governance Committee?
The strongest committees combine business, technology, legal, risk, and operational perspectives.
Typical permanent or recurring members may include.
CIO or CTO
CISO or cybersecurity leadership
AI, data, or analytics leadership
Legal counsel
Compliance
Enterprise risk
Privacy or data-protection representatives
Procurement or vendor-management teams
Relevant business-unit leaders
The exact membership should reflect the organization’s risk profile rather than copying a generic international model.
Business Owners and AI System Owners
Committee approval does not transfer operational responsibility away from the business.
Every AI system should still have a named owner responsible for its.
Business purpose
Data use
Controls
Monitoring
Human review
Incident response
Remediation
This helps prevent a common governance gap: treating committee approval as permanent permission rather than a controlled decision tied to defined conditions.
How Roles May Differ Across Saudi Arabia, the UAE, and Qatar
GCC organizations should adapt committee membership to the regulatory and operational environment in which they work.
Saudi enterprises may need to connect AI oversight with SDAIA, NDMO, PDPL, cybersecurity, and sector-specific obligations.
UAE organizations may need to account for federal requirements alongside frameworks or regulators relevant to environments such as DIFC, ADGM, digital government, or specific regulated sectors.
In Qatar, organizations particularly financial institutions may need to integrate AI governance with requirements and guidance from bodies such as QCB, MCIT, or QFC where applicable.
What Should an AI Governance Committee Charter Include?
An effective AI governance committee charter should remove ambiguity before difficult decisions arise.
Mandate, Scope, Membership, and Quorum
The charter should define.
Committee purpose
Systems and use cases within scope
Chair and executive sponsor
Permanent members
Subject-matter experts
Quorum requirements
Voting or consensus rules
Secretariat responsibilities
It should also explain when a use case can be handled through a lighter review process and when formal committee approval is required.
Decision Rights and Escalation Paths
The committee’s authority should be explicit.
Depending on the organization’s governance model, it may be empowered to.
Approve a use case
Approve it with conditions
Request additional evidence
Require remediation
Pause deployment
Reject a proposed deployment
Escalate unresolved risk to executive management, enterprise risk, or a board committee
Without defined decision rights, committees can easily become discussion forums rather than functioning governance bodies.
Evidence, Reporting, and Audit Requirements
Governance decisions should leave an auditable trail.
Useful records include.
AI inventory
Risk assessments
Approval decisions
Conditions of approval
Exception records
Vendor assessments
Security and privacy reviews
Testing evidence
Monitoring records
AI risk register
For organizations looking to scale enforcement, Mak It Solutions’ AI policy as code for enterprise control explains how policy requirements can be translated into measurable technical controls.
How Should an AI Governance Committee Assess and Approve AI Risk?
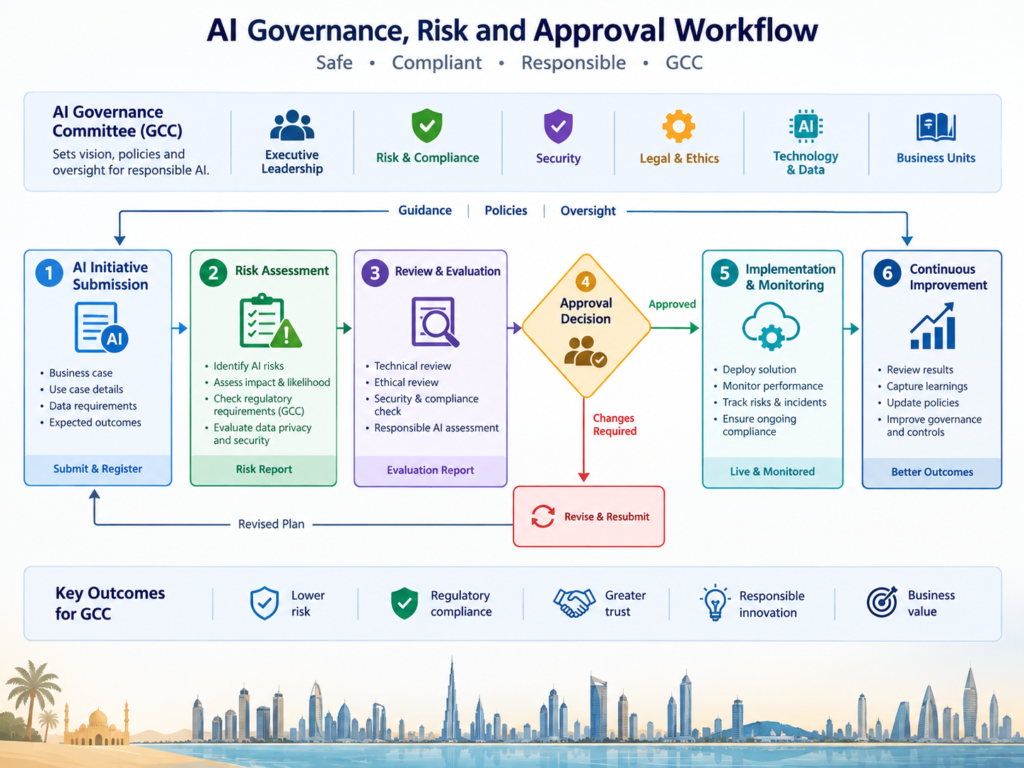
A committee works best when approvals follow a repeatable workflow rather than relying on case-by-case judgment alone.
Create an AI Inventory and Risk-Tiering Model
Start with visibility.
The organization should know what AI systems are already in use, what data they process, who owns them, which vendors are involved, and how much impact their outputs can have.
Risk tiers may consider factors such as.
Customer impact
Automated decisions
Sensitive or personal data
Financial consequences
Legal implications
Critical business processes
Generative AI exposure
External-facing outputs
Degree of human oversight
A low-risk internal productivity assistant should not necessarily undergo the same review as an AI system affecting credit, healthcare, citizen services, or financial decisions.
Define a Risk-Based Approval Workflow
A practical approval sequence is.
Identify → Register → Classify → Assess → Review → Approve or Escalate → Monitor
This creates a clear path from initial discovery to ongoing oversight.
Lower-risk tools may qualify for streamlined approval, while higher-impact applications should trigger deeper reviews involving legal, privacy, security, compliance, model-risk, and business stakeholders.
Build Human Oversight Into Approval
Human oversight should not be added as an afterthought.
Before approval, the committee should know.
Who reviews AI outputs
Who can override recommendations
Which decisions require human confirmation
What thresholds trigger escalation
What changes require reassessment
When the system must be suspended or retired
The AI adoption roadmap for GCC teams provides a useful implementation companion for organizations connecting governance with wider AI adoption.
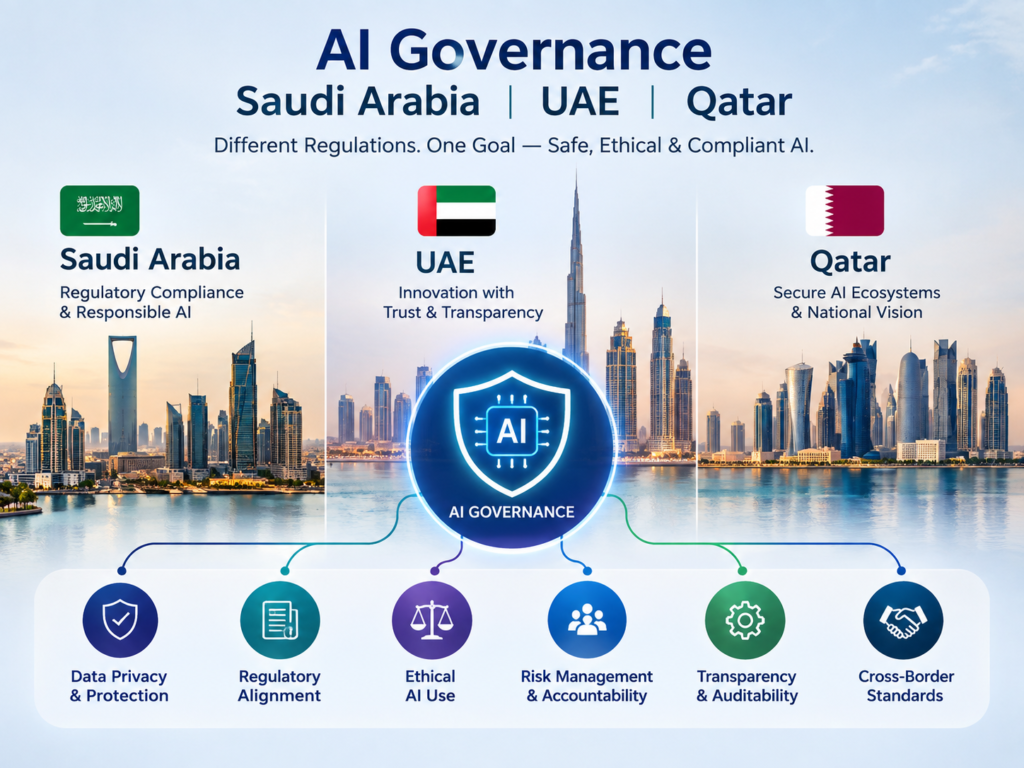
How to Align AI Governance With Saudi, UAE, and Qatar Requirements
An AI governance committee should not operate separately from existing privacy, cybersecurity, risk, and data-governance responsibilities.
Saudi Arabia.
For a Saudi organization, committee reviews may need to cover privacy, data governance, explain ability, cybersecurity, risk assessment, and accountable ownership.
SDAIA’s AI Ethics Principles address themes including privacy, transparency, accountability, security, risk management, and responsible AI practices. Saudi organizations can also use available self-assessment and data-governance resources to strengthen internal review processes.
In practice, the key is integration. AI review should connect with existing PDPL, data-management, cybersecurity, and sector-specific processes rather than creating an isolated governance layer.
UAE.
UAE organizations often need governance models flexible enough to accommodate different regulatory environments.
A Dubai fintech, an Abu Dhabi government-related entity, and a private-sector e-commerce company may all use AI differently and therefore require different review and escalation paths.
The committee should map each AI system to the requirements that actually apply to its sector, location, data, and operating model while maintaining common enterprise-level standards for responsible and safe AI use.
Qatar.
Qatar-based organizations should similarly connect AI governance with applicable national and sector-specific requirements.
For financial institutions, QCB-related AI governance expectations can make formalized assessment, system categorization, risk management, and oversight especially important.
Other organizations may also need to consider MCIT guidance, applicable QFC data-protection requirements, and broader national AI initiatives when designing their governance structure.
GCC AI Governance Controls the Committee Should Prioritize
Regional governance is not only about policies. The committee also needs to challenge practical architecture, vendor, language, and operating risks.
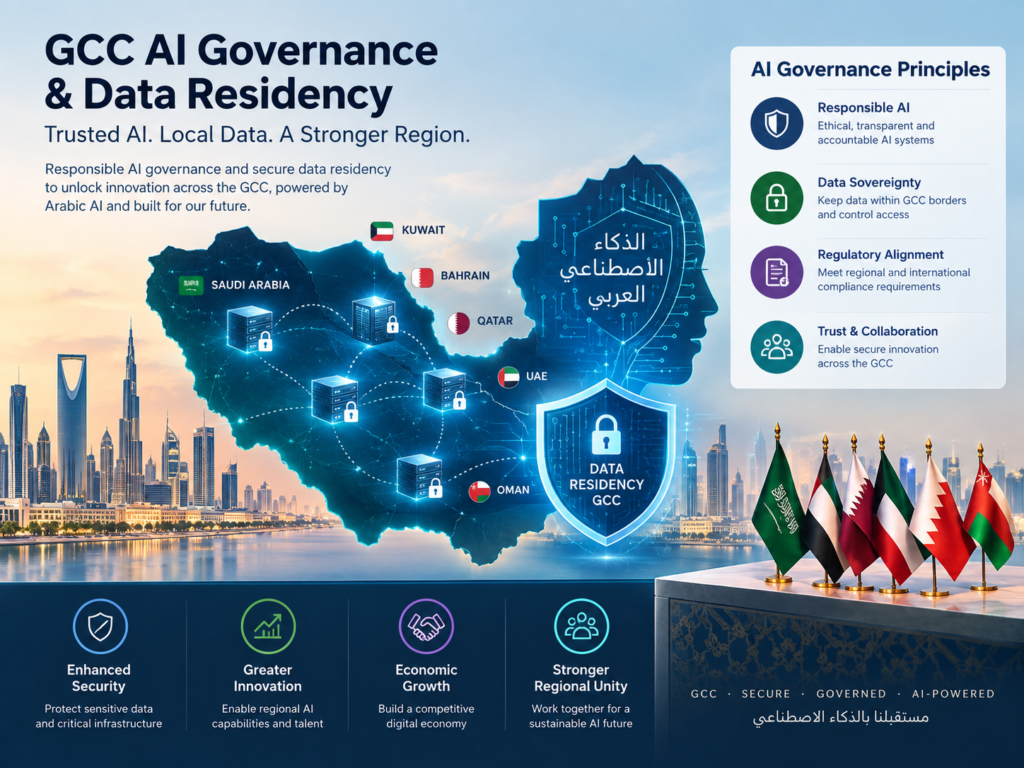
Data Residency, Privacy, and Cross-Border AI Processing
For any third-party or cloud-based AI system, the committee should ask.
Where are prompts stored?
Where are logs and embeddings stored?
Does the vendor use customer inputs for model training?
Which sub processors can access the data?
How long is information retained?
Can data be deleted on request?
Are cross-border transfers involved?
Does the architecture meet applicable legal and contractual requirements?
Regional cloud infrastructure can help organizations design appropriate architectures, but data residency should still be assessed workload by workload.
Mak It Solutions’ GCC cloud strategy guide explores these broader cloud and infrastructure considerations.
Arabic AI Accuracy, Bias, and Cultural Context
AI systems used in the GCC should be tested for the environment in which people will actually use them.
Testing may need to cover.
Modern Standard Arabic
Gulf dialects
Arabic-English code-switching
Regional names
Local terminology
Cultural context
Hallucination rates
Differences in output quality between Arabic and English
Responsible AI in the GCC is not only about technical accuracy. Language and cultural context can materially affect output quality and user trust.
Third-Party GenAI and Shadow AI
Generative AI risk often enters the organization through vendors rather than internally developed models.
Tools such as Copilot, Gemini, OpenAI-powered applications, and AI assistants embedded inside SaaS platforms should be subject to appropriate procurement and governance gates.
Vendor due diligence should examine issues such as.
Data retention
Training-data use
Model providers
Sub processors
Security controls
Contractual responsibilities
Audit evidence
Incident notification
Administrative controls
The GenAI vendor risk due-diligence guide provides a practical structure for these reviews.
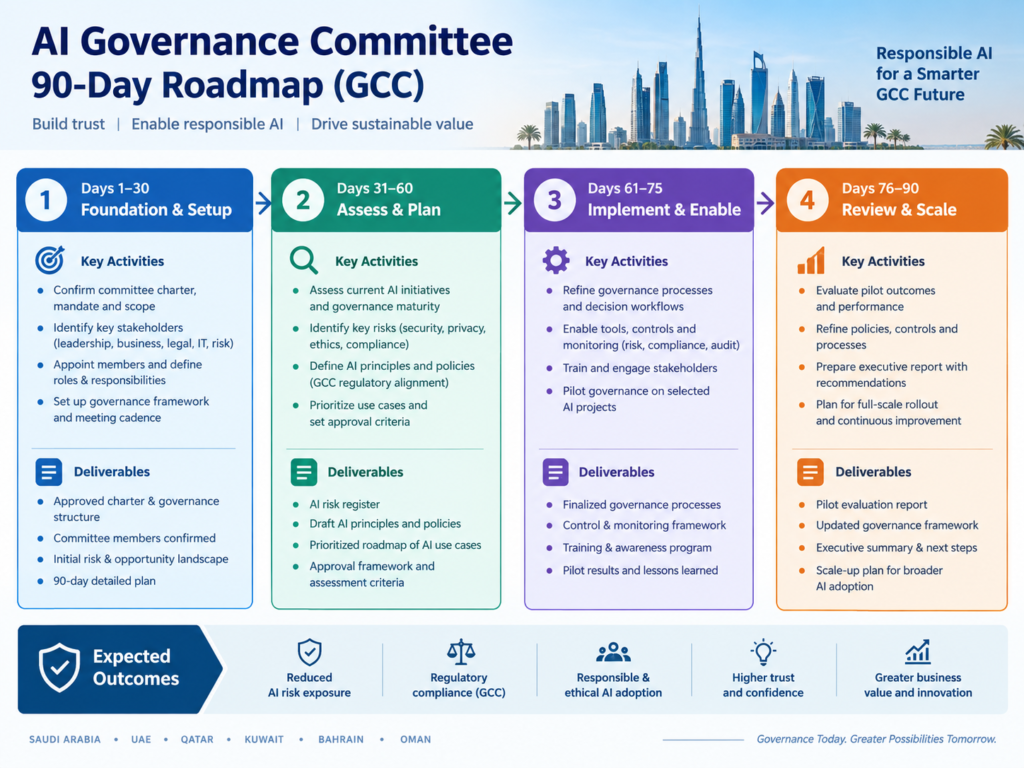
How to Launch an AI Governance Committee in the First 90 Days
A new committee does not need to solve every governance problem immediately. A staged rollout is usually more practical.
Establish Ownership and Inventory
Start by building the governance foundation.
Key actions include.
Appoint an executive sponsor
Nominate the committee chair
Confirm permanent members
Draft the committee charter
Build the initial AI inventory
Map existing privacy, cybersecurity, procurement, and risk policies
Identify known shadow-AI use
The goal is visibility and accountability before complexity.
Define Risk Tiers and Approval Rules
Next, turn governance into a repeatable process.
Create.
AI risk tiers
RACI ownership
Approval criteria
Escalation rules
Vendor-assessment requirements
Evidence standards
Exception procedures
AI risk register
At this stage, teams should know which systems require committee review and what evidence must be provided.
Run Pilot Reviews and Establish KPIs
Test the governance model against realistic use cases.
Examples might include.
A Riyadh fintech reviewing AI under financial-sector controls
A Dubai e-commerce company deploying AI-powered customer experiences
A Doha company assessing cloud and data-location requirements
An Abu Dhabi government workflow requiring human oversight
Useful governance KPIs may include AI registrations, high-risk reviews, approval turnaround times, exceptions, shadow-AI discoveries, open remediation items, and overdue reassessments.
Supporting controls can also draw on Mak It Solutions’ Zero Trust strategy for AI-era security and Business Intelligence services for access control, reporting, and governance visibility.
Concluding Remarks
A strong AI governance committee gives GCC enterprises a practical mechanism for turning responsible-AI principles into documented decisions.
The most effective model brings business, technology, legal, privacy, security, risk, compliance, and procurement together around one clear process: identify AI, classify its risk, review the evidence, assign accountability, approve appropriately, and continue monitoring after deployment. ( Click Here’s )
For organizations operating across Saudi Arabia, the UAE, or Qatar, governance should also reflect local privacy, data, cybersecurity, and sector requirements rather than relying on a generic global template.
Mak It Solutions can support organizations with AI governance maturity assessments, committee-charter workshops, AI risk reviews, vendor governance, and custom GCC AI strategies designed around their operating environment.
FAQs
Q : What should an AI governance committee charter include in Saudi Arabia?
A : A Saudi AI governance committee charter should define its mandate, membership, quorum, decision rights, escalation paths, evidence requirements, and accountability. It should also explain how AI reviews interact with privacy, cybersecurity, data governance, PDPL responsibilities, and applicable sector requirements.
Q : How often should an AI governance committee meet in a GCC enterprise?
A : The right cadence depends on AI volume and risk. A business launching several customer-facing or high-impact AI systems may require frequent meetings, while a smaller organization may operate on a less frequent schedule supported by an urgent escalation process for incidents, vendor changes, or material model updates.
Q : Does a UAE company need a separate committee for generative AI?
A : Not always. Generative AI can often be governed through the same enterprise AI governance committee if its charter explicitly covers risks such as confidential prompts, hallucinations, copyright concerns, vendor use of data, autonomous actions, and human review. A specialist working group may be useful where deployment volume or sector exposure is higher.
Q : How should Qatar companies govern third-party AI vendors?
A : Qatar organizations should assess AI vendors before procurement and continue reviewing them after deployment. Due diligence should cover data location, model providers, sub processors, security, retention, deletion, incident notification, auditability, and contractual responsibility, together with applicable QCB, QFC, or other regulatory requirements.
Q : Who remains accountable after an AI governance committee approves an AI system?
A : The named business and system owners remain responsible for operating the AI within its approved boundaries. They should monitor performance, maintain controls, manage incidents, complete required reassessments, and escalate material changes in the model, vendor, data, use case, or risk environment.