AI Agent Access Reviews: A Smarter Risk Framework
AI Agent Access Reviews: A Smarter Risk Framework
AI Agent Access Reviews: A Smarter Risk Framework
AI agents can read sensitive data, call APIs, update records, trigger workflows, and increasingly take action without a person approving every individual step. That makes AI agent access reviews a much more active security requirement than the traditional annual permissions check.
A practical approach is to combine continuous monitoring with event-driven reassessment and scheduled human certification. A privileged production agent may justify a 30-day review cycle, while a tightly scoped, read-only agent may fit a 90-day cycle. The review interval should follow the risk—not an arbitrary calendar.
For organizations developing broader identity controls, Mak It Solutions’ Zero Trust Strategy 2026 for AI-Era Security provides additional context.
What Are AI Agent Access Reviews?
An AI agent access review verifies whether an agent still needs its identities, data access, tools, OAuth scopes, roles, and privileged capabilities. It also identifies permissions that are excessive, unused, inherited unnecessarily, or no longer connected to an approved business purpose.
The objective is straightforward: every capability an agent retains should support a legitimate, current task.
How AI Agent Access Differs From Human and Service-Account Access
Human access usually maps to a person’s job responsibilities. Traditional service accounts typically perform relatively predictable machine-to-machine tasks.
AI agents can be more dynamic. Depending on their design, they may choose tools, interpret instructions, chain multiple actions, interact with external systems, or work semi-autonomously.
That makes identity and lifecycle governance especially important. Microsoft Entra Agent ID, for example, now provides purpose-built identity constructs for AI agents, including access governance, activity monitoring, lifecycle controls, owners, and accountable human sponsors.
What an AI Agent Permission Review Should Check
A useful review should examine more than the role displayed next to the agent’s name. Check.
Unique agent identity and accountable owner or sponsor
Approved business purpose and lifecycle status
Production, development, or sandbox environment
Effective RBAC and ABAC permissions
OAuth scopes and delegated authority
Connected databases, SaaS platforms, APIs, and MCP servers
Inherited or downstream permissions
Credential status and expiration
Just-in-time access and temporary elevation
High-impact actions the agent can perform
Unused or dormant entitlements
Logging, monitoring, approval, and revocation controls
Microsoft’s current guidance similarly recommends least-privilege permissions and periodically reviewing and right-sizing agent access.
Access Review vs. Permission Audit vs. Runtime Authorization
These controls solve different problems.
An access review is a formal certification that existing access remains justified. A permission audit establishes what access currently exists. Runtime authorization determines whether a particular action should be allowed at the moment it is attempted.
Mature environments need all three. Scheduled certification cannot replace runtime enforcement, while runtime policies do not remove the need for accountable human oversight.
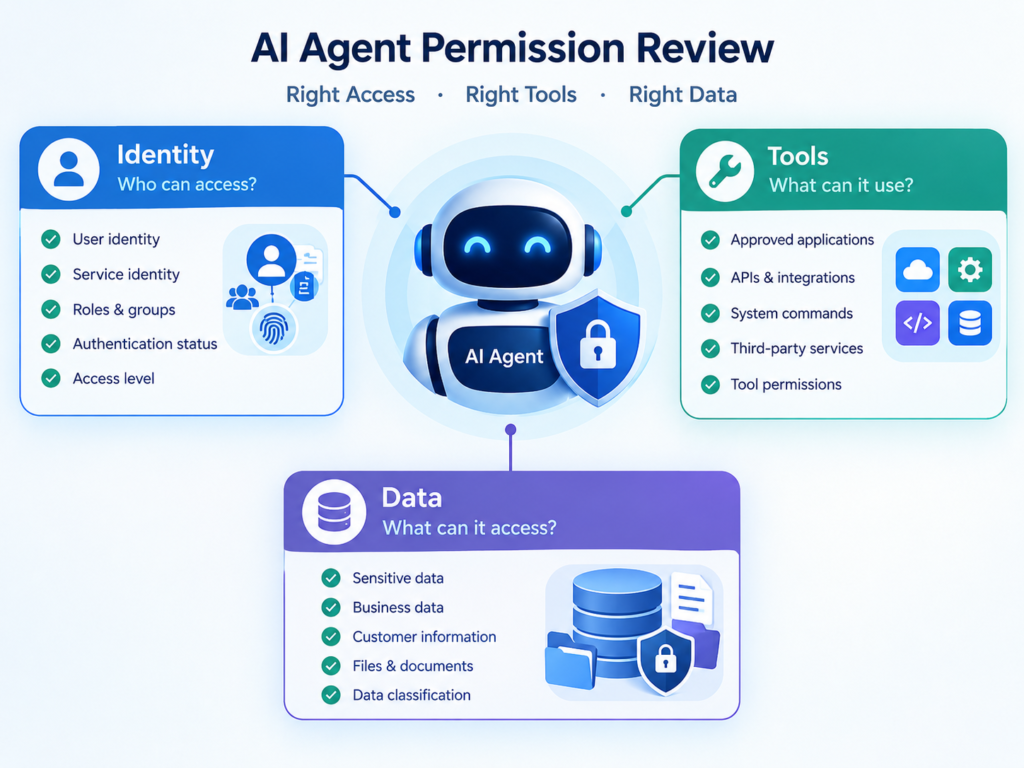
How Often Should AI Agent Access Reviews Be Performed?
There is no sensible single review interval for every AI agent. Review frequency should reflect the agent’s privilege, autonomy, data sensitivity, write capability, integration depth, and potential blast radius.
Why One Review Frequency Does Not Fit Every Agent
A read-only reporting assistant presents a different risk profile from an autonomous agent that can change production infrastructure or initiate financial transactions.
Factors that should influence frequency include.
Sensitivity of accessible data
Read versus write privileges
Production access
Level of autonomy
Transaction or operational impact
Number and power of connected tools
Ability to change identities or permissions
Downstream system access
Reversibility of actions
Regulatory and contractual obligations
The principle is consistent with risk-based governance approaches such as the NIST AI Risk Management Framework rather than treating one fixed permission-review interval as universally appropriate.
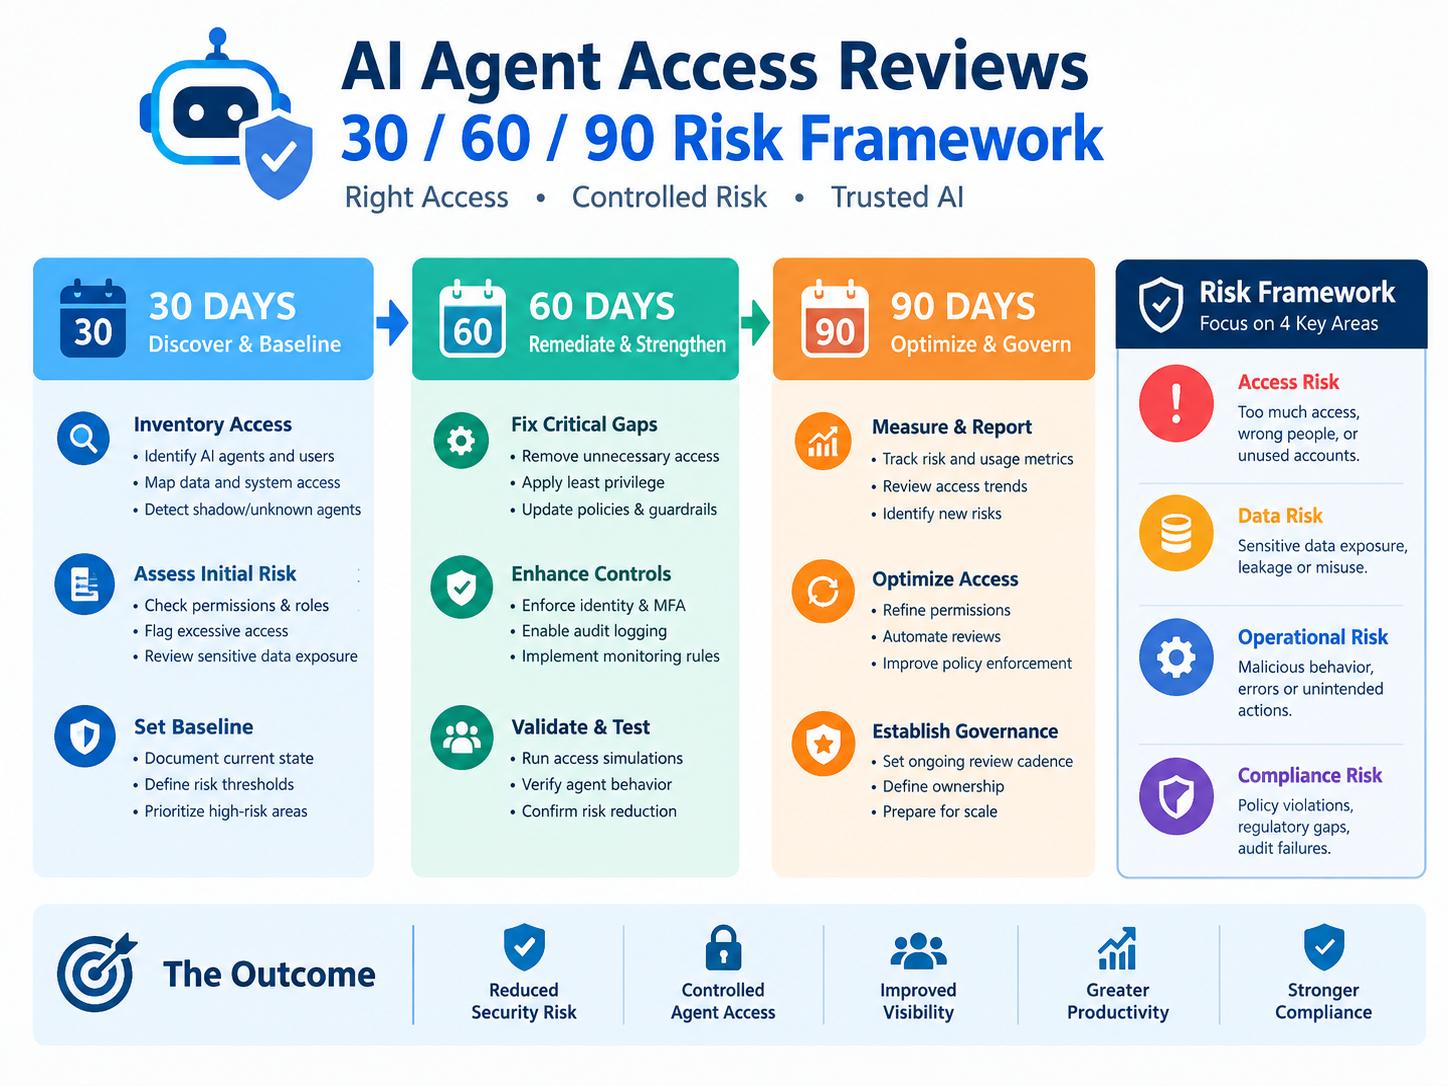
A Practical 30/60/90-Day Risk Framework
A 30/60/90-day model can provide a useful internal governance baseline.
| Review cycle | Typical risk profile | Example access |
|---|---|---|
| 30 days | High risk or privileged | Production controls, payments, security administration, sensitive personal or healthcare data, broad write privileges |
| 60 days | Medium risk | Controlled write access, departmental automation, moderately sensitive SaaS or data integrations |
| 90 days | Lower risk | Stable, tightly scoped, read-only access with clear ownership and limited downstream authority |
These periods are governance targets, not universal regulatory deadlines. Organizations should adapt them to their architecture, contracts, sector, risk appetite, and applicable legal obligations.
Continuous Monitoring Still Matters
A scheduled review only tells you whether access was appropriate at a particular point in time. An agent’s risk can change the next day when someone adds a new API, OAuth scope, MCP tool, data source, or privileged workflow.
A stronger model combines.
Continuous monitoring of identity, permissions, and behavior
Event-driven reassessment after material changes
Scheduled human certification based on risk
The security context supports that level of attention. Verizon’s 2025 Data Breach Investigations Report analyzed more than 22,000 security incidents, including 12,195 confirmed breaches, and identified credential abuse as an initial attack vector in 22% of breaches.
Which Events Should Trigger an Immediate Access Re-Review?
Do not wait for the next scheduled certification when something materially changes the agent’s authority, ownership, environment, or risk.
Changes to Purpose, Owner, Workflow, or Environment
Trigger reassessment when an agent.
Changes business purpose
Moves to another team or sponsor
Enters production
Expands into another geography or business unit
Begins handling a new data classification
Changes from advisory to action-taking behavior
A sandbox assistant promoted to production should not inherit approval simply because its identity already exists.
Microsoft’s current agent-governance model places explicit accountability on human sponsors and supports lifecycle controls when sponsorship changes.
New Tools, MCP Servers, APIs, Data Sources, or OAuth Scopes
A new integration can substantially increase what an agent can reach.
Connections to Microsoft 365, ServiceNow, cloud infrastructure, CRM platforms, databases, internal APIs, or MCP servers should therefore trigger a review of both the new integration and any authority reachable through it.
Mak It Solutions’ API Security Best Practices 2026 for Teams covers complementary controls around authentication, OAuth, API scope, and least privilege.
Privilege Escalation, Incidents, and Permission Drift
Re-review access after.
JIT or emergency privilege elevation
Suspicious or anomalous activity
Security incidents
Credential or authentication changes
Policy changes
Role-inheritance changes
Unexpected tool usage
Failed revocation
Detected permission drift
Following an incident, coordinate identity remediation with an established Cyber Incident Response Checklist rather than treating agent access as an isolated issue.
How to Apply Least Privilege to AI Agent Permissions
Least privilege means giving an AI agent only the data, systems, and actions required for its approved purpose—and retaining that access only while it remains necessary.
Prefer Task-Scoped RBAC and ABAC
Broad administrator, owner, or editor roles are convenient during deployment but can create unnecessary exposure later.
Where the architecture supports it, bind permissions to.
Specific resources
Approved actions
Data classification
Environment
Business purpose
Transaction limits
Context or risk signals
The same principle applies to cloud IAM. Mak It Solutions’ Cloud Misconfiguration Fixes for Safer Clouds provides related remediation guidance.
Gate High-Impact Actions
Payments, account deletion, production deployment, bulk export, privilege modification, and security-configuration changes deserve stronger controls than ordinary read operations.
Depending on the workflow, safeguards can include JIT elevation, short-lived credentials, separation of duties, transaction limits, explicit approval, and tested revocation.
Human approval is particularly valuable when an action has a large impact or is difficult to reverse.
Review Effective Permissions, Not Just Assigned Roles
The role shown in an IAM console may reveal only part of an agent’s actual authority.
Effective access can also come through.
Inherited roles
OAuth tokens
Delegated user authority
Nested groups
Tool chains
MCP integrations
Downstream APIs
Shared credentials
Cloud-resource policies
Security teams should therefore evaluate platforms such as Microsoft Entra Agent ID, AWS IAM, Google Cloud IAM, Okta, SailPoint, and CyberArk based on their ability to expose, govern, certify, and revoke effective access—not merely assigned roles.
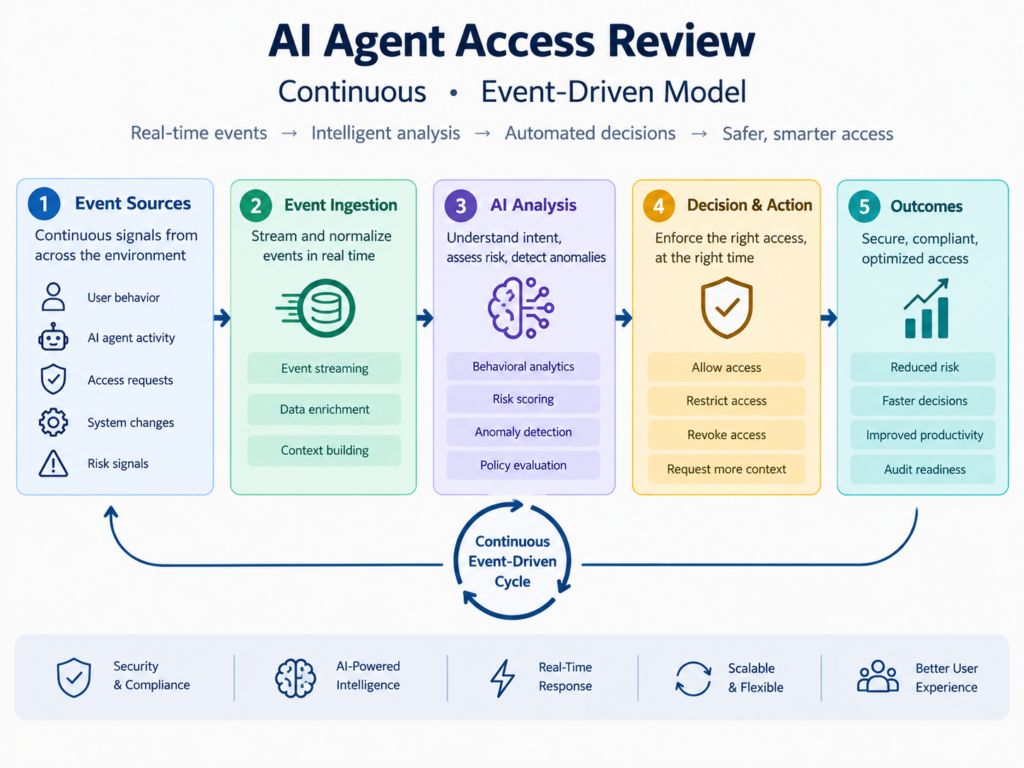
Building AI Agent Identity Governance at Enterprise Scale
Access reviews work best when they are part of a broader lifecycle rather than a recurring spreadsheet exercise.
Give Every Agent an Identity and Accountable Sponsor
Every production agent should have a unique, discoverable identity and accountable human oversight.
Its lifecycle should document.
Creation and approval
Business purpose
Owner and sponsor
Entitlement assignment
Credential management
Deployment
Access certification
Suspension
Decommissioning
Microsoft Entra Agent ID explicitly supports agent identities, human sponsorship, access governance, monitoring, and lifecycle controls.
Automate Monitoring and Certification
Automation can identify.
Dormant entitlements
Unused OAuth scopes
Excessive roles
Overdue reviews
Missing or changed owners
Policy violations
Abnormal activity
Permission drift
Those findings can then feed certification and revocation workflows rather than waiting for someone to discover the issue manually.
The data-governance challenge is already significant across complex environments. IBM’s 2024 Cost of a Data Breach research found that 40% of breaches studied involved data stored across multiple environments, including public cloud, private cloud, and on-premises systems.
Mak It Solutions’ Business Intelligence Services can also support governance dashboards and evidence reporting where organizations need centralized operational visibility.
Maintain an Audit Trail You Can Defend
Keep evidence of.
Reviewer identity
Review and approval date
Business purpose
Effective permissions
Tool and integration changes
Exceptions
Revoked access
Policy rationale
Relevant activity records
Next review date
Good evidence helps security teams answer a simple but important question: who approved this agent’s access, based on what information, and what happened after the review?
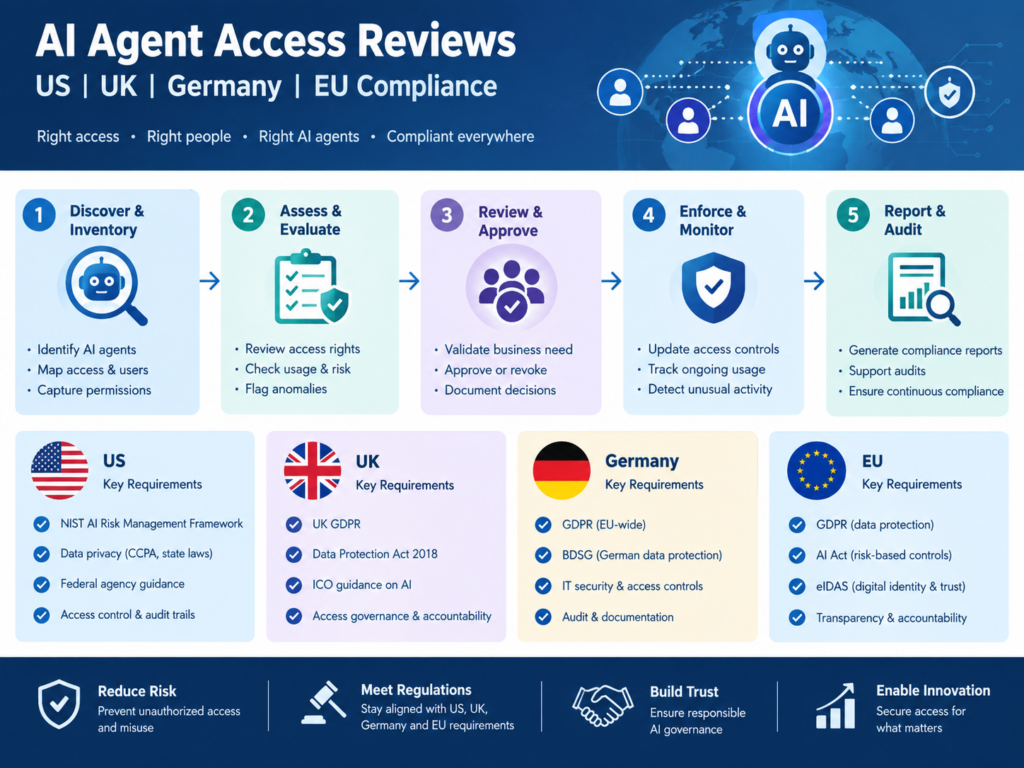
AI Agent Access Reviews in the US, UK, Germany, and EU
Organizations across these regions can use the same risk-based operating model, but legal and sector requirements still need to be mapped to the specific organization, data, and use case.
The 30/60/90-day framework should therefore be treated as an internal governance approach—not as a claim that every regulator requires those exact intervals.
United States.
A healthcare organization and a SaaS company may deploy similar agents while facing very different compliance obligations.
For organizations subject to HIPAA, the current Security Rule requires reasonable and appropriate safeguards, access controls, regular review of records relating to access, and periodic evaluation of security measures. HHS also emphasizes that compliance is an ongoing, risk-based process rather than a single universal implementation strategy.
That supports a risk-based access-review model without turning the 30/60/90-day framework into a HIPAA requirement.
United Kingdom.
For UK organizations, access governance should connect identity control with data minimisation, accountability, security monitoring, and risk management.
Current ICO guidance says access to personal data should be understood, limited to those who need it, removed when no longer needed, and checked against documented access rights. The ICO also emphasizes regular testing and a risk-based approach rather than a one-size-fits-all security model.
Endpoint security can complement these controls; see Mak It Solutions’ EDR Implementation Guide for USA, UK & EU.
Germany and the European Union
For organizations operating in Berlin, Munich, Frankfurt, Paris, Amsterdam, Dublin, and elsewhere in the EU, KI-Agenten Berechtigungen prüfen can form part of a wider Zugriffskontrolle and identity-governance program.
Document Zugriffsrechte, perform regular Berechtigungsprüfung, record privileged Freigabe, and ensure prompt Widerruf when access is no longer justified.
Depending on the organization and use case, GDPR/DSGVO, the EU AI Act, NIS2, DORA, BaFin requirements, BSI guidance, and sector rules may all influence the surrounding control framework. The practical point remains the same: determine the applicable obligations first, then document a defensible risk-based review cadence rather than presenting 30/60/90 days as a universal legal mandate.
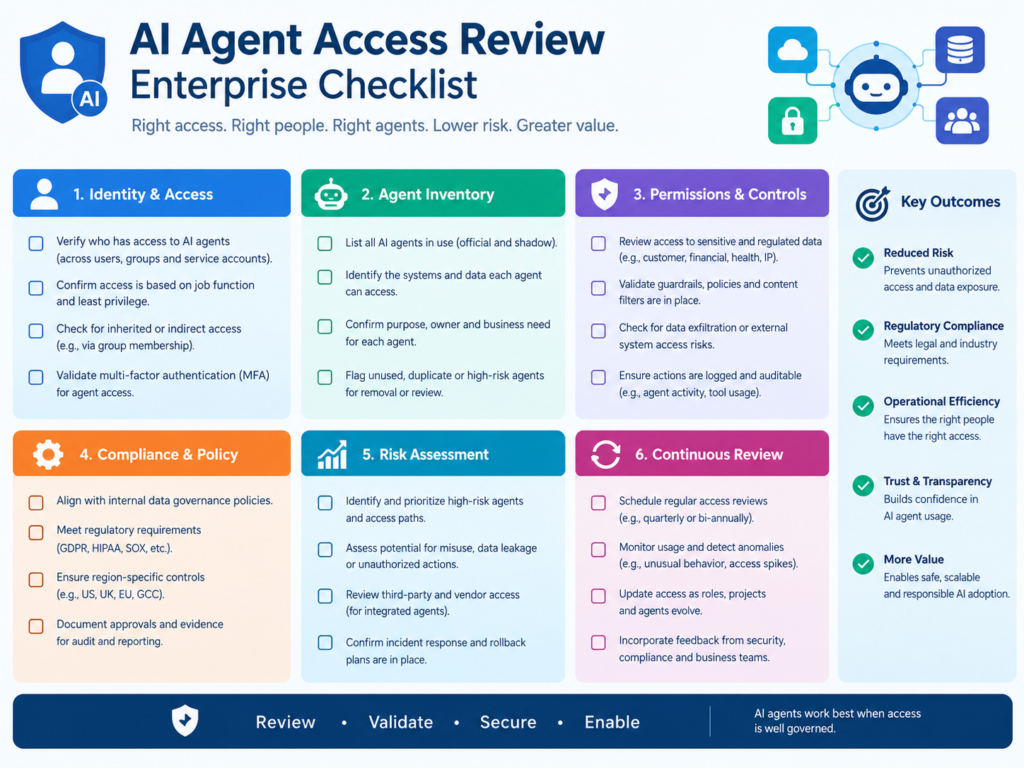
AI Agent Access Review Checklist for Enterprises
A repeatable review process can be organized around three control areas.
Identity and Ownership
Confirm.
Unique agent identity
Accountable sponsor and technical owner
Approved purpose
Deployment environment
Lifecycle status
Authentication method
Credential status
Permissions, Tools, and Data
Review.
RBAC and ABAC assignments
OAuth scopes
MCP tools and servers
SaaS integrations
APIs and databases
Delegated authority
Write privileges
Inherited permissions
Unused entitlements
Monitoring, Revocation, and Evidence
Validate.
Activity monitoring
Anomaly alerts
JIT workflows
Human approval gates
Credential expiration
Revocation capability
Exceptions
Audit evidence
Next certification date
At scale, automate four connected capabilities: agent inventory, risk classification, change triggers, and certification/revocation workflows.
Organizations developing supporting platforms can explore Mak It Solutions’ broader technology services.
Final Thoughts
AI agent access reviews are becoming a core part of modern identity governance as organizations give AI systems more autonomy, data access, and operational authority. A risk-based 30/60/90-day review framework helps teams match review frequency to privilege level, business impact, and data sensitivity while combining scheduled certification with continuous monitoring and event-driven reassessment.
The strongest approach focuses on least privilege, clear ownership, effective-permission visibility, reliable revocation, and documented audit evidence. By treating AI agent access reviews as an ongoing governance process rather than a periodic checkbox, enterprises can reduce permission drift, improve accountability, and strengthen security across complex environments.
AI agent governance becomes easier when identity inventory, permission monitoring, AI agent access reviews, certification, and revocation operate as one connected workflow.
Mak It Solutions can help assess your current AI and cloud access model and translate it into a scoped, risk-based governance roadmap.
Request a scoped consultation with Mak It Solutions.
Key Takeaways
AI agent access reviews should not be reduced to an annual checkbox.
A stronger governance model combines scheduled certification, continuous monitoring, and immediate reassessment when material changes occur. The 30/60/90-day framework gives teams a practical starting point: shorter cycles for privileged and high-impact agents, and longer cycles for stable, tightly scoped, lower-risk agents.
Just as importantly, review effective permissions across OAuth, APIs, MCP tools, delegated access, RBAC/ABAC, and downstream systems not only the role shown in an identity console.
Every production agent should ultimately have a clear purpose, accountable human oversight, least-privilege access, reliable revocation, and an audit trail that explains why its access remains justified.
FAQs
Q : Who should approve an AI agent’s permissions during an access review?
A : The accountable business sponsor should confirm that the access remains necessary for the agent’s purpose, while security or IAM teams validate the technical permissions and policy requirements. Higher-risk agents may also require approval from data owners, application owners, compliance teams, or privileged-access administrators.
Q : Which AI agents should require human approval before privileged actions?
A : Human approval is particularly appropriate when an agent can move money, modify production infrastructure, delete data, change permissions, export sensitive records, administer accounts, or perform other high-impact actions that may be difficult to reverse.
Q : What evidence should be retained after an AI agent access review?
A : Keep the agent identity, sponsor, review date, reviewer, approved purpose, effective permissions, tools, OAuth scopes, data sources, exceptions, changes made, revoked entitlements, and next review date. Higher-risk environments may also retain relevant approval and activity records.
Q : How can organizations detect unused or excessive AI agent permissions?
A : Compare the agent’s entitlement inventory with actual usage. Flag dormant permissions, broad roles, unused OAuth scopes, unnecessary MCP tools, inherited privileges, and unexpected downstream access, then validate the findings before removing access needed for legitimate but infrequent workflows.
Q : When should AI agent access be revoked automatically?
A : Automatic revocation can be appropriate when an agent is decommissioned, temporary access expires, required ownership disappears, or policy clearly prohibits the access. Where compromise is suspected, immediate suspension may be appropriate while security teams investigate.